

A question that has been on the minds of the cybersecurity community in Greece since yesterday: is there really a Mikel Coffee ransomware incident or is it an unconfirmed claim? The well-known coffee chain Mikel Coffee, with over 410 stores in 19 countries, appears on a list of victims of the TheGentlemen. The entry was published on August 9 and 10, 2026 on ransomware monitoring platforms. There has been no official confirmation from the company itself, and the gang's claims currently remain unconfirmed. The SecNews editorial team presents the available data with the clear caveat that the claim has not been independently verified.
Read also: Eurobank phishing SMS: Customers in the spotlight

What TheGentlemen claims about Mikel Coffee ransomware
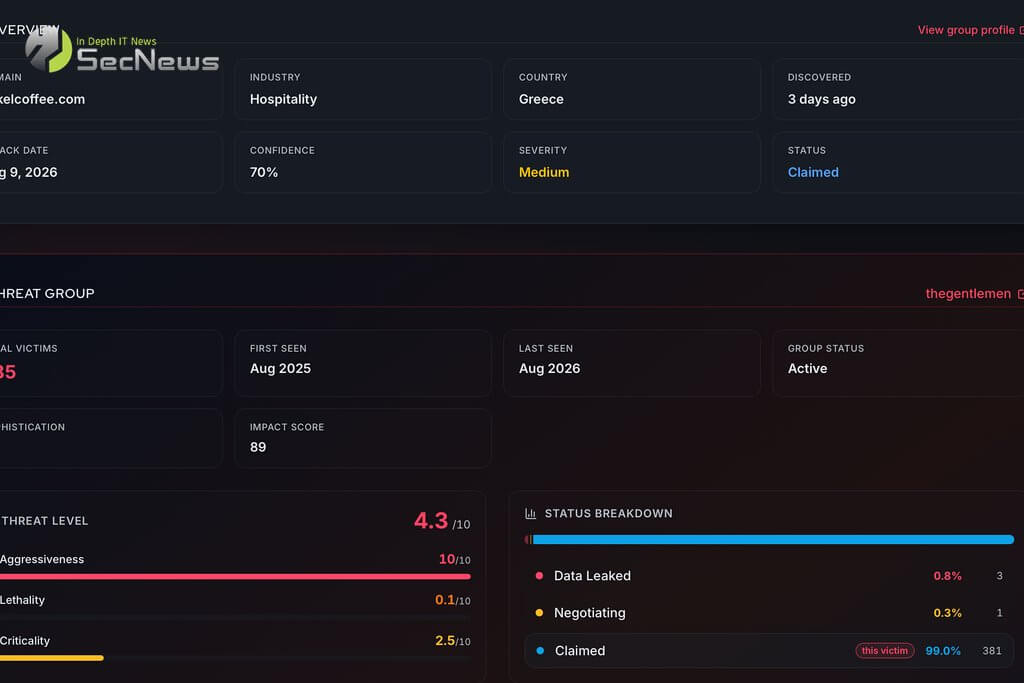
According to data from threat intelligence platform SOCRadar, the incident was first detected three days ago, with an attack date of August 9, 2026. SOCRadar classifies the case with 70% confidence, medium severity, and a status of “Claimed.” A similar record appears on GalaxyWarden with a disclosure date of August 9, on RecentBreaches with a public report date of August 10, on HookPhish and on DeXpose.
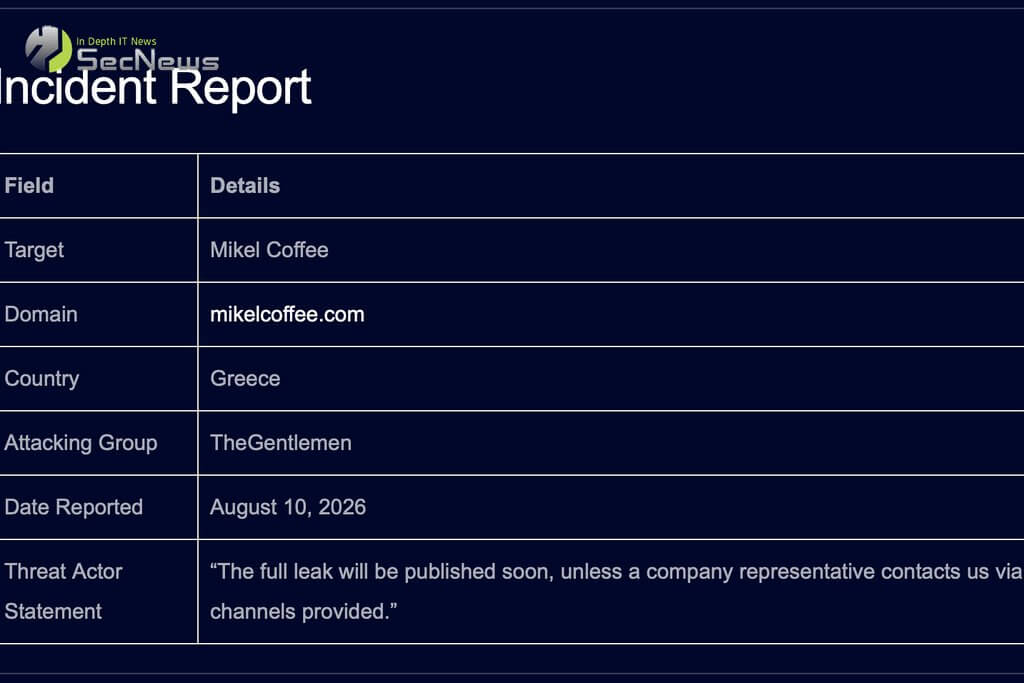
The attackers’ statement attributed to TheGentlemen states verbatim, according to DeXpose: “The full leak will be published soon, unless a company representative contacts us through the channels provided.” No working data sample has been released, no specific volume in gigabytes has been mentioned, and no public deadline for payment of the ransom has been set.
The group claims to have obtained files containing customer data, with at least one password field. It has not disclosed operational credentials, does not state a specific amount of data in gigabytes, and has not publicly set a deadline for payment. There is no indication that session tokens, API keys, unencrypted passwords, or credit card information were exposed.
The most important point is that, as all the trackers explicitly state, this information is a gang claim, not a confirmed leak. No company or regulatory authority has confirmed the existence of an incident. Mikel Coffee has not made a public announcement.
What is the role of TheGentlemen ransomware?
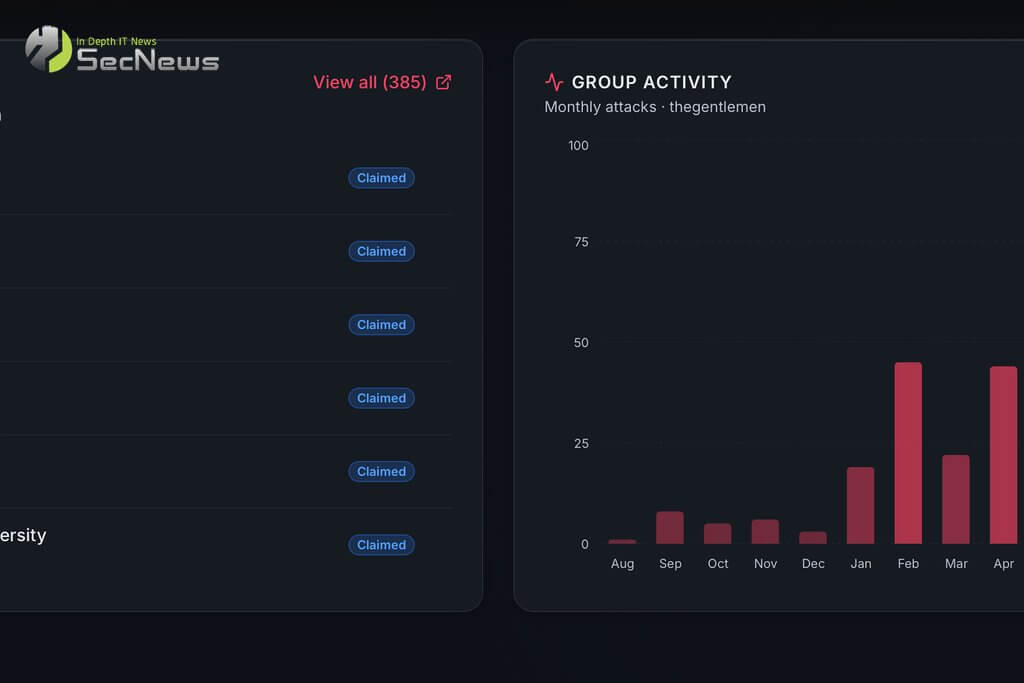
TheGentlemen is a ransomware-as-a-service group active since August 2025. According to SOCRadar data, the group has registered a total of 385 victims with an average of almost 30 attacks per month, while its status remains “Active” and the peak of activity was recorded in July 2026 with almost 100 new reports. According to research by The Hacker News in June 2026, the group had then registered 478 victims on its dark web leak page. More recent analyses by Palo Alto Networks Unit 42, which tracks the group as Storm-2697, put the number at over 580 victims in 77 countries by early July 2026. Check Point Research ranks it as the second most active ransomware group of the year.
The group operates on an affiliate model, offering an unusually high 90/10 ratio of ransomware revenue to the affiliate. This generous distribution has attracted a significant number of attackers and explains its rapid expansion. Its targets are geographically dispersed, with only 13% located in the US. The majority of victims are concentrated in Thailand, the UK, Brazil, Germany and India.
A notable detail from the same research: TheGentlemen malware includes self-propagation capabilities, making it extremely difficult to stop after initial penetration. An internal leak of the group’s chats in May 2026 revealed their full playbook, but did not stop their activity.
What is Mikel Coffee and why might it interest you?
Mikel Coffee Company was launched in 2008 in Larissa and has grown into one of the largest Greek coffee chains, with a presence in 410+ stores in 19 countries. It operates a loyalty program via a mobile app, where users create an account, record transactions and collect points. The potential number of affected individuals includes thousands of customers with active accounts on the app.
If the claim is verified, the case would be classified as a special category due to the scale of personal data potentially exposed and the obligation to notify the Data Protection Authority within 72 hours of becoming aware of the breach, under the GDPR. Currently, no such notification has been made public.
The scenarios that remain open
At this stage, three scenarios remain possible. First, the entry corresponds to a real incident that the company is investigating internally before making a public announcement. Second, it is a partial penetration of a part of the system without significant data removal, with the gang exaggerating its claims for reasons of negotiating pressure. Third, the claim is empty or concerns a third-party service provider in the chain, not the company itself.
Ransomware gangs often inflate their claims or publish reused data from previous attacks to increase pressure for payment. The group itself has a history of leaking its claims, according to an internal playbook exposed in May.
What customers can do proactively
Regardless of whether the claim is verified or not, Mikel Coffee customers who maintain an account on the app should take precautionary measures. The first step is to immediately change the password on the relevant app. If the same password is used on other services, such as email, banking applications or e-shops, the change should be extended there as well.
☁️ Keep safe copies with Proton Drive
Encrypted cloud storage from Proton — protect your files from ransomware, corruption, and data loss with end-to-end encryption.
- ✔ End-to-end encrypted files & backups
- ✔ Version history — recover files after ransomware
- ✔ Free space — sync across all devices
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
The second step is to enable two-factor authentication (2FA) where supported. The SecNews technical team recommends preferably authenticator applications such as Google Authenticator or Authy, or even better physical security keys (YubiKey), instead of SMS which is vulnerable to SIM-swap attacks. At the same time, users who do not have an active relationship with Mikel Coffee can delete their account after changing their password.
Step three: carefully monitor bank and credit card transactions for at least 30 days. If the same credit card is used for payments through the app, enabling real-time transaction alerts via bank push notifications is an important defense.
Related: iPhone 18 pre-order scams: How to protect yourself
The reservations held by the SecNews team
Serious cybersecurity media outlets are wary of ransomware claims. Presenting reports on leak sites as confirmed breaches without an official announcement from the company or notification to the relevant authorities can create unnecessary panic or, conversely, legitimize them by strengthening their bargaining position.
Mikel Coffee’s official position, whatever it ultimately is, will determine what happens next. If the company confirms the incident, the next steps include an investigation with the assistance of ENISA and the Greek Data Protection Authority. If, on the contrary, it turns out that this is a false or exaggerated claim, the case will be added to the long list of impressive but untrue reports from ransomware groups.
Customers with questions can contact Mikel Coffee's official service channels.
Useful: Delta Air Lines: WiFi turned off at DEF CON
