

While macOS is still considered by many to be a highly secure operating system, cybercriminals are now developing more sophisticated techniques specifically targeting Mac. One of the latest threats is PamStealer, a new infostealer that, according to researchers at Jamf Threat Labs, introduces a particularly dangerous approach: it verifies that the password the victim types is valid before proceeding to steal personal data.
This feature significantly increases the value of stolen credentials, as perpetrators know from the very beginning that they have functional login details.
Disguise in a popular app
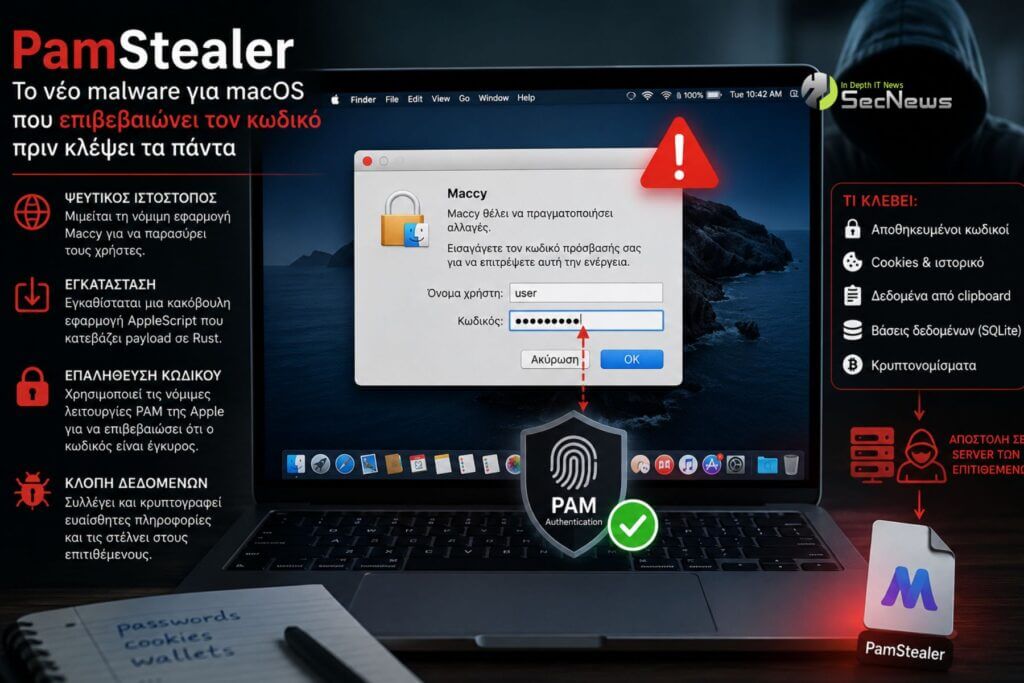
The PamStealer distribution campaign relies on social engineering . Attackers create a fake website that closely mimics the legitimate Maccy clipboard manager, tricking users into downloading a supposedly legitimate program.
See also: Apple working on Mac Studio M7 Ultra for 2028 with possible major upgrade
In fact, the file that is installed is a malicious AppleScript. Once executed, it performs initial checks on the system and retrieves a second payload, which has been developed in the Rust. From there, the malware is permanently installed on the system, ensuring that it will continue to run even after the computer is restarted.
Targeted attacks instead of mass distribution
Another feature that makes PamStealer stand out is that it does not activate indiscriminately on every computer. Before performing its basic functions, it examines various macOS parameters, such as system characteristics, keyboard layout, and regional settings.
This behavior suggests that its creators are interested in specific targets rather than a generalized infection campaign, while also limiting the chances of the malware being detected by security researchers.
PamStealer: The innovation lies in the code verification
The element that most differentiates PamStealer from other infostealers is the credential collection process.
The malware displays a window that looks exactly like the authentic macOS authorization window, asking the user for the administrator password to supposedly make changes to the application.
See also: M5 Ultra Mac Studio to be released in 2026 with up to 768GB of RAM
However, it doesn't just store what the user types. Instead, it leverages Apple's legitimate PAM (Pluggable Authentication Modules ) system to verify that the password is actually correct . It doesn't break or bypass the operating system's authentication mechanism, but rather exploits its legitimate capabilities, offering attackers instantly verified credentials.
Extensive collection of personal data
Once verification is complete, the second stage of the malware begins collecting sensitive information. Its targets include cookies and browsing history, saved passwords, SQLite databases, clipboard contents, and data from cryptocurrency wallets.
Before being sent to the attackers' servers, all data is encrypted, making it difficult for both security experts to detect suspicious network traffic and analyze the attack.
At the same time, PamStealer attempts to gain "Full Disk Access" rights, even impersonating Finder, in order to gain access to even more of the user's files without additional restrictions.
🔑 Secure your passwords with Proton Pass
Password manager from Proton — end-to-end encryption, passkeys, built-in 2FA, and monitoring for leaks of your credentials.
- ✔ Encrypted storage of passwords & passkeys
- ✔ Notification if any of your passwords are leaked (Dark Web Monitoring)
- ✔ Free version — on all devices
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
Rust makes analysis difficult
The researchers point out that much of the second stage has been developed in Rust, a choice that is not accidental. This language makes difficult reverse engineering, as many critical strings and execution paths are only revealed during program execution and not in the final binary.
This trend has been observed more and more frequently in recent years, as several cybercriminal groups choose Rust to increase the complexity of their attacks and delay the development of detection tools.
See also: Steam: Mac game developers need to update

What users should watch out for
The PamStealer case proves that modern threats are not necessarily based on unknown vulnerabilities, but on the abuse of legitimate functions of the operating system itself and, above all, on deceiving the user.
Protection starts with downloading applications only from trusted sources, thoroughly checking the address of each website before any installation, and treating any unexpected request for an administrator password with extreme caution. It is equally important to grant the “Full Disk Access” permission only when absolutely necessary and to applications from trusted developers. Finally, regularly updating macOS and security solutions remains one of the most effective ways to promptly detect and block known threats.
