

A new malware strain called BundleBot operates by exploiting .NET file deployment techniques, allowing threat actors to steal sensitive information from infected computers.
See also: Roblox: Previous data breach exposed 4000 users' details
Some of these websites aim to imitate Google Assistant, the company's artificial intelligence robot, by tricking victims into downloading a fake RAR file (“Google_AI.rar”) hosted on legitimate cloud storage services, such as Dropbox.
The archive file, when unzipped, contains an executable file (“GoogleAI.exe”), which is a single-file, self-contained .NET application, which, in turn, embeds a DLL file (“GoogleAI.dll”) responsible for retrieving a password-protected ZIP file from Google Drive.
See also: Two critical AMI MegaRAC vulnerabilities identified
The contents of the extracted ZIP file (“ADSNEW-1.0.0.3.zip”) are another single-file, self-contained .NET application (“RiotClientServices.exe”) that embeds the BundleBot payload (“RiotClientServices.dll”) and a command and control (C2) packet data serializer (“LibrarySharing.dll”).
The binary artifacts use specially crafted obfuscation and junk code in an attempt to resist analysis and have the capabilities to extract data from web browsers, take screenshots, steal Discord tokens, Telegram information , and Facebook account details .
Check Point reported that it has also detected a second BundleBot sample that is almost identical in all aspects, except for the use of HTTPS to leak information to a remote server in the form of a ZIP file.
This development comes as Malwarebytes uncovered a new campaign that uses sponsored posts and has compromised verified accounts, which impersonate Facebook Ads Manager to trick users into downloading rogue Google Chrome extensions designed to steal Facebook login information
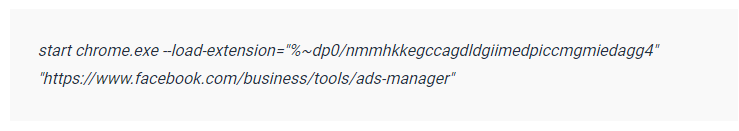
Users who click on the embedded link are prompted to download a RAR archive file containing an MSI installation file which, in turn, launches a batch script to create a new Google Chrome window with the malicious extension loaded using the “–load-extension” flag.
The captured data is then sent through the Google Analytics API to bypass content security policies (CSPs) to mitigate Cross-Site Scripting (XSS) and data injection attacks.
See also: Mallox ransomware exploits weak MS-SQL servers to compromise networks
The threat actors behind the activity are believed to be of Vietnamese origin and have shown a keen interest in targeting business and advertising accounts on Facebook in recent months. Over 800 victims worldwide, including 310 in the US, have been affected.
Information source: thehackernews.com
