

Users who download MSI Afterburner from unofficial websites risk infecting their computers with cryptocurrency miners and the information-stealing RedLine malware.
See also: Ducktail:Phishing campaign via WhatsApp targets Facebook Ad Accounts

MSI Afterburner is a handy tool for graphics card users that allows you to adjust overclocking, create fan profiles, record videos, and monitor GPU temperature and CPU usage.
Tweak your game settings, make your graphics card run quieter, and lower its temperature using this utility created by MSI. It is popular among gamers worldwide because it can be used with almost any type of graphics card.
See also: Microsoft warns about the dangers of Boa Web Server
Due to its success, this tool has unfortunately become a prime target for criminals looking to exploit Windows users with high-performance GPUs for cryptocurrency mining.
MSI Afterburner emulation
A recent report by Cyble states that over 50 websites have been created in the last three months, all of which appear to be the official MSI Afterburner website. These sites are promoting XMR (Monero) miners along with info-stealing malware.
The campaign used domains that led users to believe they were on MSI’s official website. These types of domains are easier to promote with BlackSEO tactics, some examples of which Cyble found are listed below:
- msi-afterburner–download.site
- msi-afterburner-download.site
- msi-afterburner-download.tech
- msi-afterburner-download.online
- msi-afterburner-download.store
- msi-afterburner-download.ru
- msi-afterburner.download
- mslafterburners.com
- msi-afterburnerr.com
Other times, the domains bore no resemblance to the MSI brand and were likely promoted through instant messaging, forums, and social media posts. Some examples include:
- git[.]git[.]skblxin[.]matrizauto[.]net
- git[.]git[.]git[.]skblxin[.]matrizauto[.]net
- git[.]git[.]git[.]git[.]skblxin[.]matrizauto[.]net
- git[.]git[.]git[.]git[.]git[.]skblxin[.]matrizauto[.]net
Stealth mining while stealing your passwords
When the fake MSI Afterburner setup file (MSIAfterburnerSetup.msi) is executed, it will install the legitimate Afterburner program. However, the installer will drop and silently execute the RedLine information-stealing malware and an XMR miner on the compromised device.
The miner is installed via a 64-bit Python executable file named 'browser_assistant.exe' in the local Program Files directory, which allows it to take control of the processes created by the installer.
This shellcode retrieves the XMR miner from a GitHub repository and injects it directly into memory in the explorer.exe process. Since the miner never touches the disk, the chances of it being detected by security products are minimized.
The miner connects to his mining pool using a coded username and password, and then collects and feeds key system data to the threat actors.
The XMR miner is designed to use as much CPU power as possible, by setting the 'CPU max threads' argument to 20, which exceeds the number of threads of most modern CPUs.
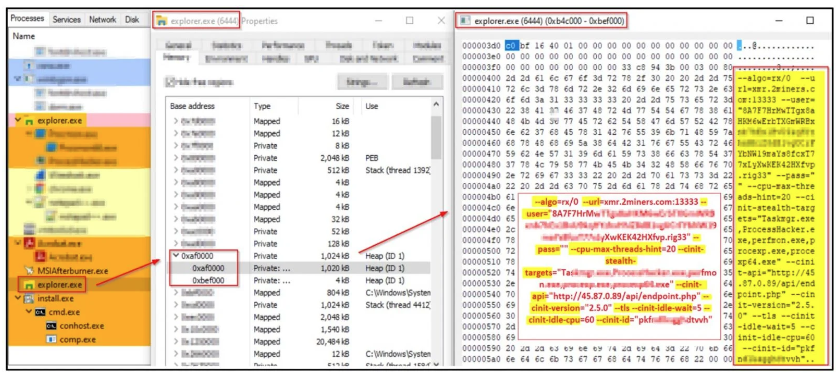
The miner will only activate after the CPU has been idle for 60 minutes, which suggests that the infected computer is not being used for demanding tasks.
See also: Mali GPU: 'Patch gap' leaves Android users exposed
The Windows applications that the miner tries to hide from are Taskmgr.exe, ProcessHacker.exe, perfmon.exe, procexp.exe, and procexp64.exe.
As the miner cunningly uses your computer's resources to mine Monero, RedLine quickly steals your passwords, cookies , browser information – possibly even your cryptocurrency wallets .
The best way to avoid downloading malware is to only visit the official websites of the tools you want to download.
MSI Afterburner can only be downloaded directly from MSI at www.msi.com/Landing/afterburner/graphics-cards to avoid scams.
Information source: bleepingcomputer.com
