

Over 3.6 million MySQL servers are publicly exposed on the Internet and respond to queries, making them an attractive target for hackers.
See also: Samsung releases June 2022 security patches to Galaxy S21

Of these accessible MySQL servers, 2.3 million are connected via IPv4, with 1.3 million devices via IPv6.
Although it is common for web services and applications to connect to remote databases, these instances should be locked down so that only authorized devices can connect to them.
See also: Ethical hackers: Industrial systems are not safe for the future
Additionally, public server exposure should always be accompanied by strict user policies, changing the default access port (3306), enabling binary logging, monitoring all queries closely, and enforcing encryption.
3.6 million MySQL servers exposed
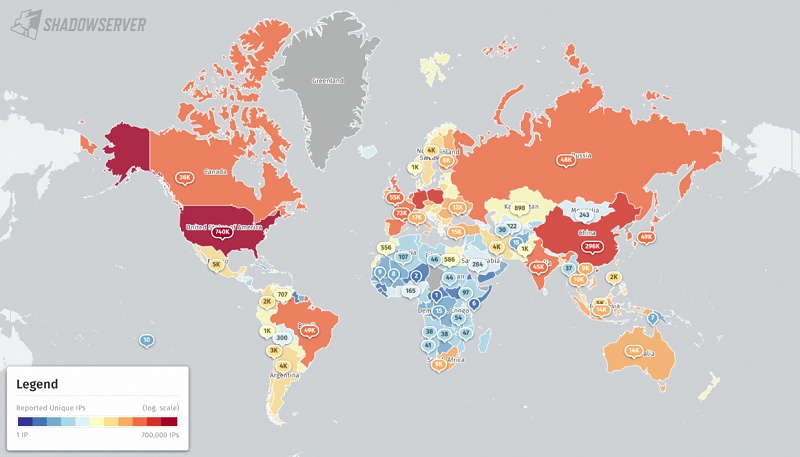
In scans conducted last week by cybersecurity research group The Shadowserver Foundation, analysts found 3.6 million exposed MySQL servers using the default TCP port 3306.
“While we do not control the level of access or exposure of specific databases, this type of exposure is a potential attack surface that should be closed,” the report from Shadow Server explains.
The country with the most accessible MySQL servers is the United States, with over 1.2 million. Other countries with significant numbers are China, Germany, Singapore, the Netherlands , and Poland.
To learn how to securely deploy MySQL servers and close security holes that may be lurking in your systems, Shadow Server recommends that administrators read this guide for version 5.7 or this one for version 8.0.
Data brokers who sell stolen databases told BleepingComputer that one of the most common vectors of data theft is databases that are insecure, which the administrator should always lock down to prevent unauthorized remote access.
See also: Microsoft Office zero-day: Used in PowerShell execution attacks
Failure to secure MySQL database servers can lead to catastrophic data breaches, destructive attacks, ransom, remote access trojan (RAT) , or even Cobalt Strike.
All of these scenarios have serious consequences for affected organizations, so it is important to implement appropriate security practices and remove your devices from being accessible with simple network scans.
Information source: bleepingcomputer.com
