

GoodWill ransomware was detected by CloudSEK researchers in March 2022. As the threat group's name suggests, its operators are reportedly interested in promoting social justice rather than conventional financial reasons.
See also: Hackers use deep fake videos of Elon Musk in crypto scam
A new ransomware strain has been detected in India that tricks victims into donating clothes to the homeless and providing financial assistance to anyone in need of urgent medical care but unable to afford it, according to digital risk monitoring firm Cloudsek. The firm warned that the Goodwill ransomware could lead to both temporary, and possibly permanent, loss of corporate data and a potential shutdown of company operations and accompanying loss of revenue.
See also: Sberbank says it faces huge waves of DDoS attacks
After infection, the GoodWill ransomware worm encrypts documents, photos, videos, databases , and other important files and makes them inaccessible without the decryption key.
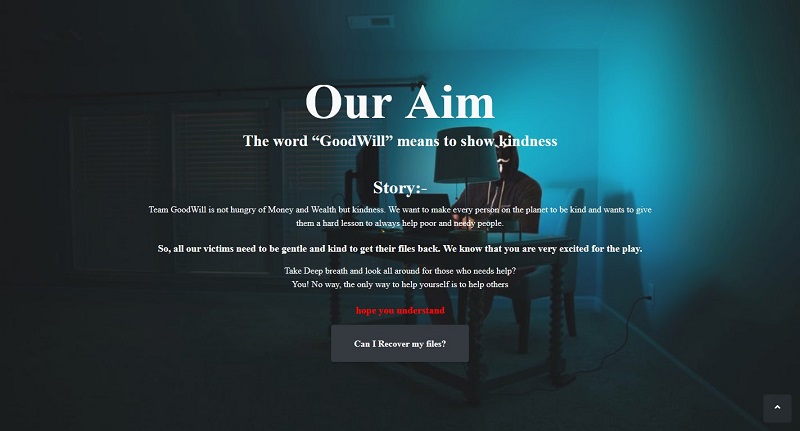
“The hackers suggest that victims do three social activities in exchange for the decryption key – donate clothes to the homeless, record the action and post it on social media, take five underprivileged children to Dominos Pizza Hut or KFC and treat them, take photos and videos and post them on social media, and provide financial assistance to anyone who needs urgent medical care but cannot afford it, at a nearby hospital, record an audio document and share it with the operators,” the report said.
Once all three activities are completed, the ransomware asks victims to make a post on social media (Facebook or Instagram) about “how you transformed yourself into a kind human being by becoming a victim of a ransomware called GoodWill.”
See also: Microsoft: Huge increase in Linux XorDDoS malware activity
Upon completion of all three activities, ransomware operators verify the media files shared by the victim and their social media posts
The hacker will then share the full decryption kit that includes the main decryption tool, the password , and a video tutorial on how to recover all important files, the report said.
"Our researchers were able to trace the email address provided by the ransomware group to an solutions and services company that provides end-to-end managed security services," the report said.
Information source: businessinsider.in
