

A new hacking group called Moses Staff has recently claimed responsibility for numerous attacks against Israeli entities, which appears to be politically motivated as it is not demanding a ransom.
Threat actors have repeatedly caused damage to Israeli systems over the past two months, infiltrating networks and encrypting files, then leaking the stolen copies to the public.
Therefore, the group's obvious motive is to cause maximum operational disruption and damage to its targets by revealing corporate secrets and other sensitive information through dedicated data leak websites, Twitter accounts, and Telegram channels.
See also: Robinhood: Millions of customer data sold on hacking forum

Publicly available information
Researchers at Check Point published a detailed report today on the Moses Staff group, examining the techniques, infection chain, and toolset used by the group.
The Moses Staff team appears to be using publicly available exploits for known vulnerabilities that remain unpatched in public-facing infrastructure.
For example, the hacking group is targeting vulnerable Microsoft Exchange servers that have been under exploitation for months, yet many deployments remain unpatched.
See also: Docker servers targeted by hacking group TeamTNT
After successfully compromising a system, threat actors will move laterally through the network with the help of PsExec, WMIC, and Powershell, so no custom backdoors are used.
The hackers ultimately use a custom PyDCrypt malware that uses DiskCryptor, an open-source disk encryption tool available on GitHub, to encrypt devices.
Weak encryption scheme
CheckPoint explains that encrypted files can be restored under certain circumstances, as the encryption scheme uses symmetric key generation when encrypting devices.
PyDCrypt generates unique keys for each hostname based on the MD5 hash. If the PyDCrypt copy used in the attack is recovered and reversed, the hashing function can be derived.
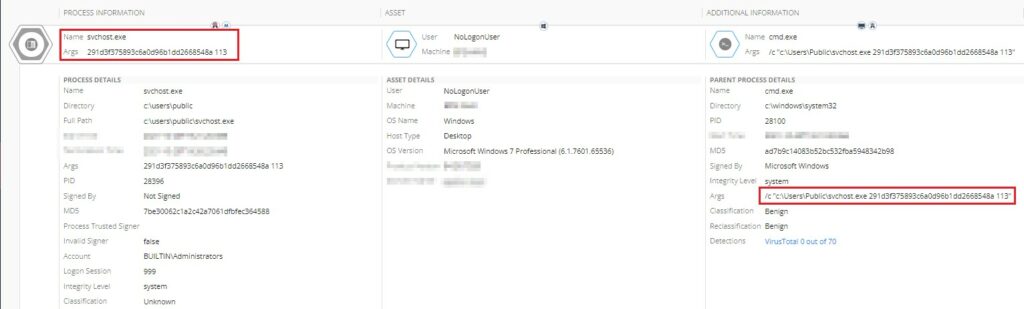
This is possible in many cases where ransomware self-deletion did not work or was disabled in the configuration.
In general, the Moses Staff team does not put much effort into this aspect of its operation, as the main thing they aim for is to cause chaos in the targeted Israeli business, not to ensure that encrypted drives are unrecoverable.
See also: This package provides all the white hat hacking knowledge you want
Political motives
Although the group is new, it may have links to “Pay2Key” or “BlackShadow,” which have the same political motivations and the same targeting scope.
So far, analysts have not been able to attribute Moses Staff to any specific geographic location or whether it is a state-sponsored group.
However, one of the malware samples used in the Moses Staff attacks was uploaded to VirusTotal from Palestine a few months before the attacks began.
As the Moses Staff attacks exploit old vulnerabilities that have patches available, Check Point advises all Israeli entities to patch their software to prevent attacks.
Information source: bleepingcomputer.com
