

A report by Amnesty International links an Indian cybersecurity company with an Android spyware program that is used for targeting prominent activists.
The research comes from the team of Amnesty International, which confirmed a espionage case against a Togo activist and also observed signs of spyware development in several key Asian regions.
See also: ACSC reports 28% decrease in overall cybersecurity incidents
A link with an Indian cybersecurity company
According to Amnesty International, the Android interception software has been linked to the Indian cybersecurity company Innefu Labs after an IP address belonging to the company was repeatedly used to distribute the spyware payload.
However, the actual deployment could be the work of «Donot Team» (APT-C-35), an Indian hacker group that has been targeting governments in Southeast Asia since at least 2018.
Amnesty notes that it is possible that Innefu does not know how its customers or other third parties use its tools. However, an external audit could reveal everything now that the full technical details have come to light.
In a written letter to Amnesty International, Innefu Labs denies any involvement with the Donot Team and the targeting of activists.
See also: Microsoft joins Space ISAC – will help with cybersecurity
Targeting of Togo activists
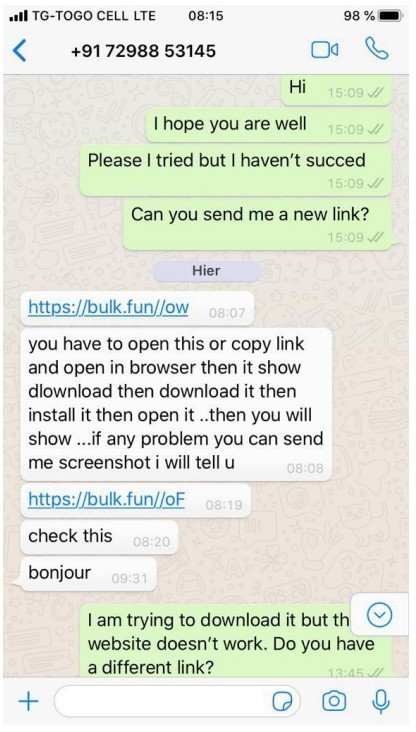
The attack on the activists began with an unsolicited message on WhatsApp, which suggests the installation of a purported secure messaging app called «ChatLite».
After failing in this way, the intruders sent an email from a Gmail account, delivering a laced MS Word file that exploits an old vulnerability to drop the spyware.
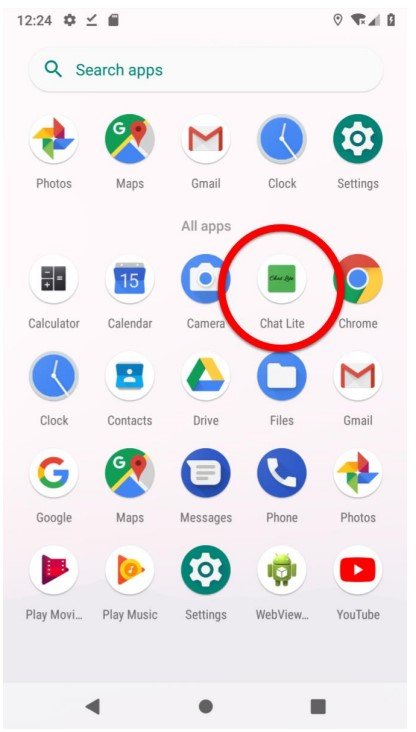
In the case of ChatLite, the spyware was a custom Android application that allowed the intruder to collect sensitive data from the device.
The spyware distributed via a malicious Word document had the following capabilities:
- Keystroke logging
- Periodic screenshot capture
- File theft from local and removable storage
- Download additional spyware modules
Analyzing the Android spyware sample, the researchers of Amnesty found several similarities with “Kashmir_Voice_v4.8.apk” and “SafeShareV67.apk”, two malware tools linked to previous operations of the Donot Team.
The mistake of the threatening factor allowed researchers to discover a “test” server in the USA, where hackers stored screenshots and keylogging data from compromised Android phones.
See also: IT: Cybersecurity budget is wasted on supporting remote work
This is where Amnesty saw the IP address of Innefu Labs for the first time, as in another case, the real source was hidden behind a VPN.
This is the first time that the Donot Team was detected targeting entities in African countries and could be an indication that the group offers «hacking for rent» services to governments.
Information source: bleepingcomputer.com
