

Kaseya has warned its customers about an ongoing phishing campaign that is attempting to compromise their networks through spam emails, which contain malicious attachments and links that appear to be legitimate security updates.
On July 2, Kaseya – which serves managed service providers (MSPs) among its customer base – was hit by the REvil ransomware, which managed to exploit vulnerabilities in the company's VSA software.
As a precaution, the company took both its VSA and SaaS servers offline. However, approximately 50 direct customers, as well as approximately 1,500 businesses, have been affected as a result of this malicious activity.
Read also: REvil ransomware Kaseya: Russians attacked 200 American companies
On July 8, the software solutions provider reported that scam artists are exploiting the security incident to send fake email notifications that appear to be Kaseya updates.
These are phishing emails that may contain malicious links and/or attachments, the company added.
Samples of fake Kaseya email, as noted by Malwarebytes, urge recipients to download and run an attachment called “SecurityUpdates.exe” to fix a vulnerability in Kaseya and protect themselves from ransomware.
See also: REvil ransomware Kaseya: Hackers demand $70 million to decrypt all systems
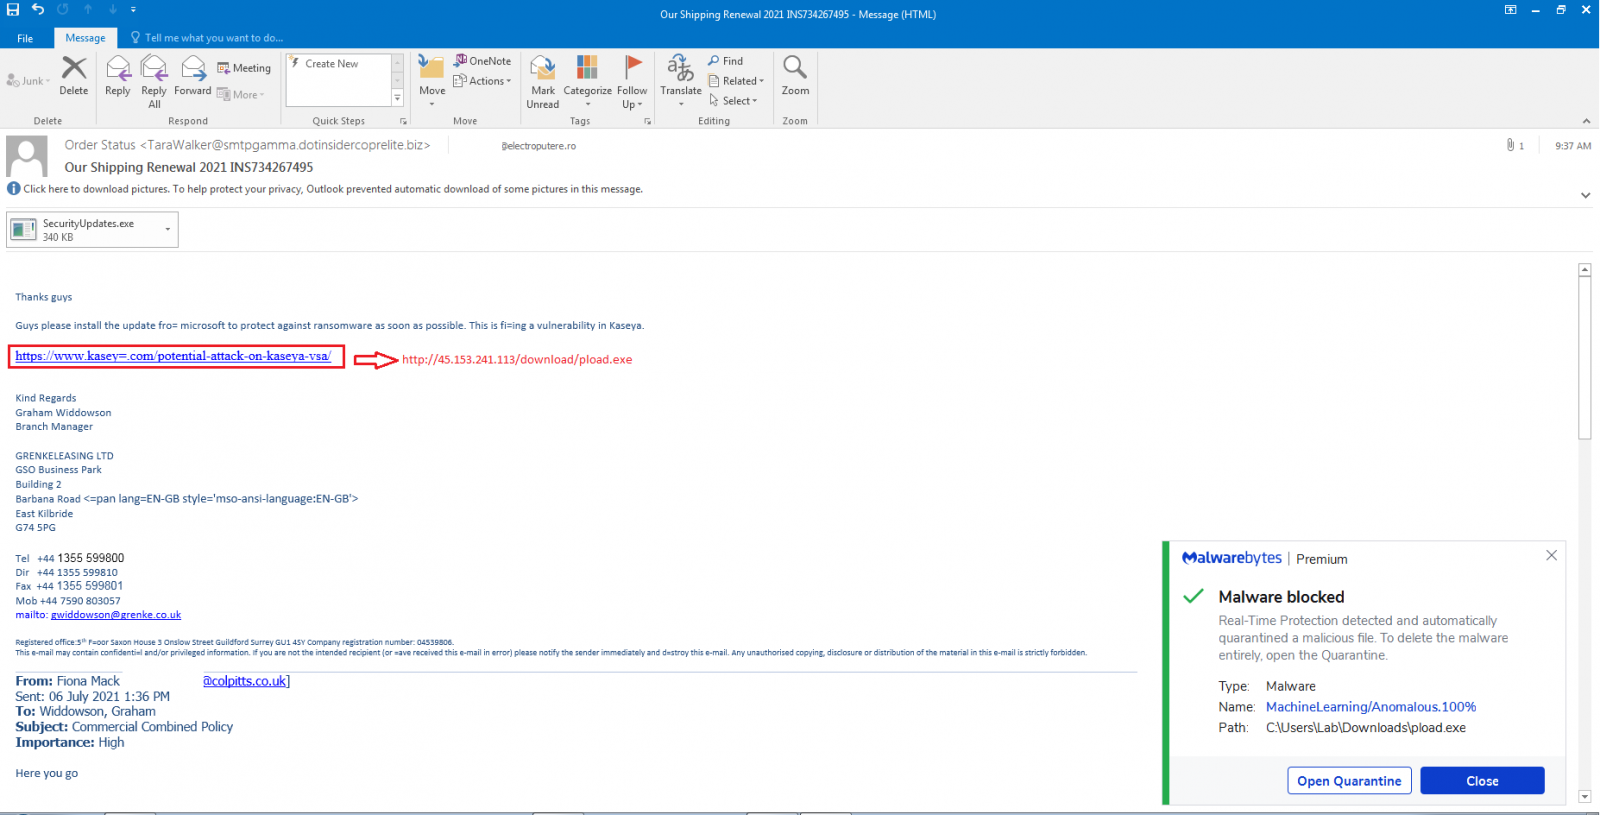
However, the attachment, a Windows executable, is actually a Cobalt Strike package. The legitimate threat simulation tool is used by penetration testers, but unfortunately, it is also widely used by malicious actors.
Cobalt Strike can be used to establish a connection to a C2 server. Along with Metasploit, an open source penetration testing toolkit – these tools were used to host over a quarter of all malware-linked C2s in 2020.
The sample email also contained a link to a malicious executable.
Suggestion: Kaseya REvil ransomware: Over 1,500 companies affected
In the past, some legitimate emails sent to customers included links that directed recipients to Kaseya's helpdesk. If customers are accustomed to this type of format, they may be more prone to clicking on malicious links sent via email by malicious actors.
In light of this potential security risk that adds to the existing burden of remediation efforts, the company says it will no longer send email updates that contain links or attachments.
Kaseya has encountered some issues during remediation efforts. In a July 8 update, Kaseya CTO Dan Timpson said that the vulnerabilities have been fixed and that additional security measures before deployment to improve the overall security posture of the company's products.
Information source: zdnet.com
