


A security expert, Stacy Arruda, gave an interview about one of the biggest threats in cyberspace, ransomware.
A few words about Stacy Arruda
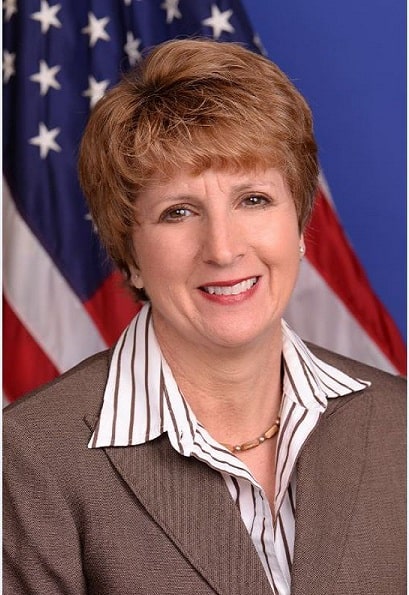
Arruda is the director of the Florida Information Sharing and Analysis Organization. The organization collects information about cybersecurity and helps victims overcome threats. She worked for the FBI for 22 years, until she retired in 2018.
The Tampa Bay Times interviewed Arruda earlier this year. According to the expert, one of the biggest threats facing and businesses local governments in Florida is ransomware:
The initial question the expert received was “what is ransomware?” Arruda said that ransomware is simply a piece of malicious code.
“Ransomware is (usually) delivered via email … And what can be attached to that email is a piece of ransomware, a piece of malicious code that compromises the network.”
“91% of all cybercrime starts with an email,” he said.
Companies and government agencies in Florida are very vulnerable to these attacks.
Another question asked of the expert was: “What are some examples of major ransomware attacks?”
“A prime example is Baltimore. … Baltimore was the victim of a ransomware attack for 14 months…”.
Arruda said that in 2019, the city's computers were infected with ransomware, which took down systems for weeks, affecting bill payment systems and more. The city was forced to pay $6 million to restore its IT systems, but it did not pay the ransom. Atlanta also faced a big problem.
Other Florida cities, such as Riveria Beach and Lake City , also paid large sums ($600,000 and $460,000 respectively).
Arruda was also asked about the relationship between social media and ransomware:
“Let’s say I have a company I want to join. And I find that there are six people in HR who have their information on LinkedIn. I can target those people. One of those six people will open the malicious email. The goal of the bad guy is to find something that the recipient would be interested in opening.”
When asked what happens if a company is infected, Arruda said there are three options. In the first case, companies have offline, have developed a robust contingency plan, and have contacts with security companies so they can call them if they have a problem. This is the good scenario and what all companies. Otherwise, they will be forced to pay the ransom, hoping to receive the appropriate decryption keys. And the third case is that companies pay the ransom and unlock their systems, but for a while. The hackers maycome back and re-encrypt the computers. Of course, there is the possibility of payment, without a response from the hackers. So the systems remain locked again.
When it comes to protecting companies and organizations from ransomware, Arruda said there is no surefire strategy. However, she added that some security measures and practices reduce the likelihood of attacks. Staff should be educated and take care not to expose information online (social media, etc.) because attacks can start there.
