

Video game companies are once again victims of the Winnti hacking group, which used new malware that researchers have dubbed PipeMon and a new method to achieve persistence.
PipeMon is a modular backdoor that was detected earlier this year on servers belonging to several massively multiplayer online (MMO) game developers.

Winnti's activity has been detected as far back as 2011. Most victims come from the video game and software, but the group also targets organizations in the healthcare and education sectors.
The group is known for supply chain attacks, targeting millions of users using software such as Asus LiveUpdate, CCleaner or in the financial sector (NetSarang).
Researchers at cybersecurity firm ESET found a new backdoor related to Winnti in February. Two variants of the malware were found on servers from South Korea and Taiwan.
The security firm is aware of at least one case where the attacker managed to compromise a system . If they had successfully infiltrated, Winnti could have installed malware within the video game.
In a report today, ESET says that the pile of evidence discovered in these attacks “clearly points” to Winnti. Despite the novelty of the PipeMon malware, the backdoor was signed using a certificate belonging to a video game company that was attacked in 2018.
This confirmation is not unique. The hackers reused some command and control (C2) domains seen in other campaigns and a custom login stealer previously seen on other Winnti victims.

Remains active in the system
Of the two PipeMon variants discovered, researchers could only determine one way to install and achieve persistence.
To ensure that the malware remained active on systems, Winnti used Windows print processors (DLLs) that convert spooled data from a "print job" into a format readable by a print screen.
A malicious DLL loader drops where the print processors are located and registers itself as an alternative print processor. This is done by modifying one of two registry values (the typo in the registry key does not affect the installation):
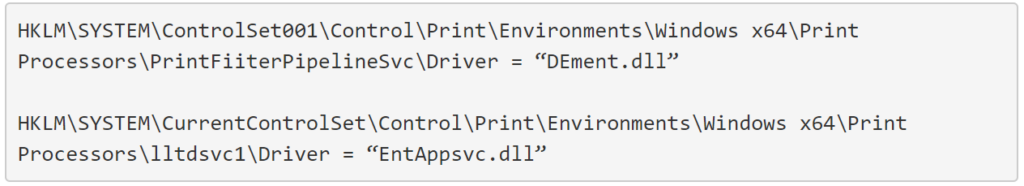
The malware then restarts the print spooler service to load the malicious process. Since the service starts every time the computer starts, persistence is achieved.
ESET notes that a similar technique was observed with the DePriMon downloader, but researchers believe that the way PipeMon works has not been implemented before.
According to the research, PipeMon is a modular backdoor, where each component is a DLL with different functionality.
They are encrypted on disk and hidden under the non-suspicious names you see below. Custom commands can load other modules on demand.
- banner.bmp
- certificate.cert
- License.hwp
- JSONDIU7c9djE
- D8JNCKS0DJE
- B0SDFUWEkNCj.logN
ESET notes that the update for PipeMon was likely written from scratch, even though they observed the same code structure.
For the past decade, Winnti has been developing its arsenal of malicious tools and carrying out attacks against various targets. Its preference for gaming companies and supply chain attacks continues to be notable in its most recent activity.
