

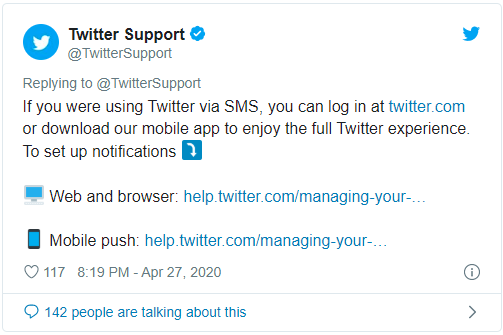
Twitter said in a statement that it has disabled the service that allows users to Tweet via SMS for security reasons. Specifically, the company said that it wants to continue to ensure that accounts remain secure. It also added that due to the fact that vulnerabilities have been reported in SMS, it has decided to disable Tweeting via SMS, with the exception of a few countries. However, the company clarified that users of the application will still be able to use “important SMS messages” to log in to the platform and manage their accounts. In addition, it is recommended that users who Tweet via SMS go to the social network platform or the Twitter mobile “to enjoy the full Twitter experience.”
For now, the company has decided not to remove two-factor authentication (2FA) and password verification. Previously, it temporarily disabled Tweeting via SMS between September 4 and 5, 2019, to protect its accounts, following the breach of the Twitter account of Jack Dorsey, CEO . Twitter noted that it has re-enabled this service for some sites that rely on SMS to Tweet, but for the rest of the world it remains disabled.
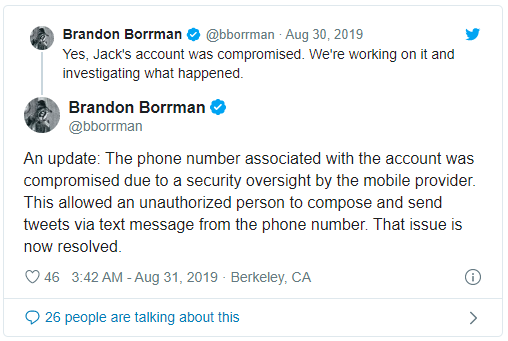
Brandon Borrman, Twitter's vice president of Global Communications, said the phone number associated with the account had been compromised due to security by the mobile carrier, allowing hackers to compose and send Tweets via SMS using Dorsey's phone number.
In February, the company discovered and fixed a bug that hackers exploited to match specific phone numbers to their corresponding Twitter accounts using a large network of fake accounts. In October 2019, Twitter revealed that some users' phone numbers and email , provided for account security purposes such as 2FA, may have been inadvertently used for ad. The company said at the time that no personal user data between it and its partners or other third parties, noting that as of September 17, it had addressed the issue that allowed this to happen, and had stopped using phone numbers or email addresses collected for security purposes.
