


Mozilla has just released an update for its Firefox browser to fix a securitythat hackers. It's a zero-day vulnerability.
If you are using the regular version of Firefox, you should upgrade from 74.0 to 74.0.1, and if you are using the Extended Support Release (ESR), you should upgrade from ESR version 68.6.0 to ESR 68.6.1.
The zero-day vulnerability could have existed since Firefox version 68, which was released in July 2019. It may, however, have been a "side effect" of a patch in version 68.0.
(If you have Firefox ESR version XY0, you essentially remain on the Firefox X.0 feature set, but with all the security that have been released up to Firefox (X + Y) .0).
However, there are no details about when the Firefox flaw was discovered by hackers and how exactly they are exploiting it.
At the moment, Mozilla only says this:
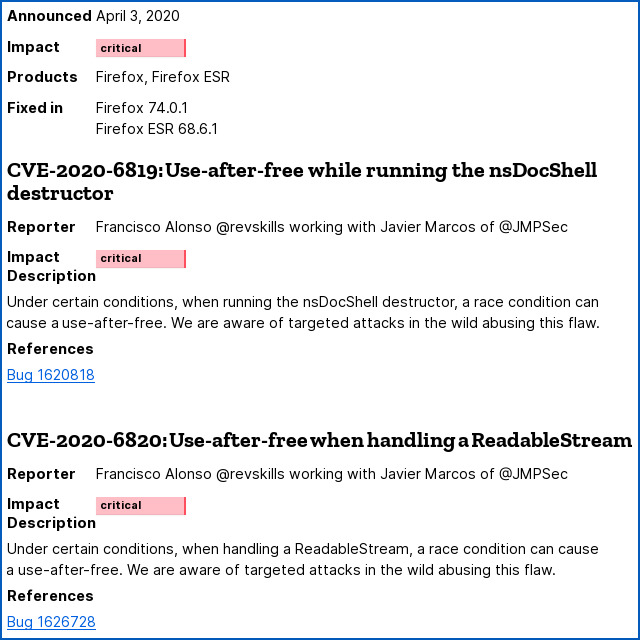
What does use-after-free mean?
Use -after-free is a class of errors caused by a of memory blocks program 's improper use .
Typically, a program "returns blocks of memory" to the operating system after it is finished with them, allowing the memory to be used again for something else.
The function by which memory is returned for reuse is called free(), and once you free the memory, you obviously cannot access it again.
In this process, a mistake can be made and you can enter code into data that was created in such a way by a fraudster to deceive you.
Not all use-after-free bugs are exploitable, and they also can't all cause the same problem. For example, an attacker could just change the content of an icon or message you want to display, which could be used to trick other users.
However, in some cases, the bugs can allow an attacker to change the flow of control within the program . For example, it could influence the CPU to execute untrusted code that the attacker "dumped" into memory, bypassing the browser 's security checks .
This is the most serious type of vulnerability. It is also known as RCE and refers to remote code execution. The criminal can execute code on your computer even if they are on the other side of the world.
What can we do?
If some hackers have already managed to exploit the vulnerability, others will do so. Therefore, the most common but effective response is to regularly update systems.
Most Firefox users should receive updates automatically, but it's a good idea to check to be sure.
Click the menu (three-line icon) in the upper-right corner, then select Help > About Firefox.
