

The North Korean hacking group Lazarus Group has targeted multiple crypto exchanges in the past year, Chainalysis reports. In March 2019, hackers stole approximately $7 million in various cryptocurrencies from Singapore. While the amount was relatively small for such an operation, the hackers went to great lengths to obtain it.
The group used a sophisticated phishing, creating a realistic website and social media presence for a fake company called WFC Proof. The supposed company had created Worldbit-bot, a trading bot that was offered to DragonEx employees.
Although the software allegedly resembled a real trading bot, it contained malware that could hijack the infected computer. The software installed itself on a machine that contained the private keys to the DragonEx wallet, allowing the hackers to steal the funds.
The attack is notable for its very specific target and execution. The hackers appear to be very experienced in cryptocurrencies, even placing an ironic warning on their website not to let anyone access personal private keys.
Quick cashout
The group was previously known for "freezing" stolen money for up to 18 months and cashing it out once the situation was safe.
In 2019, they changed their behavior, opting to cash out the funds as soon as possible. To do this, the Lazarous Group began using CoinJoin-enabled wallets to mix coins .
The hackers cashed out most of the money about 60 days after the attack, as opposed to almost a full year for the 2018 attacks.
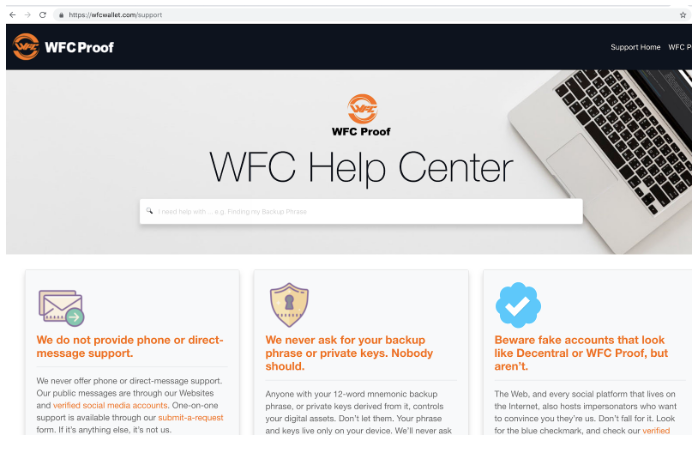
Screenshot of the fake website. Source: Chainalysis
