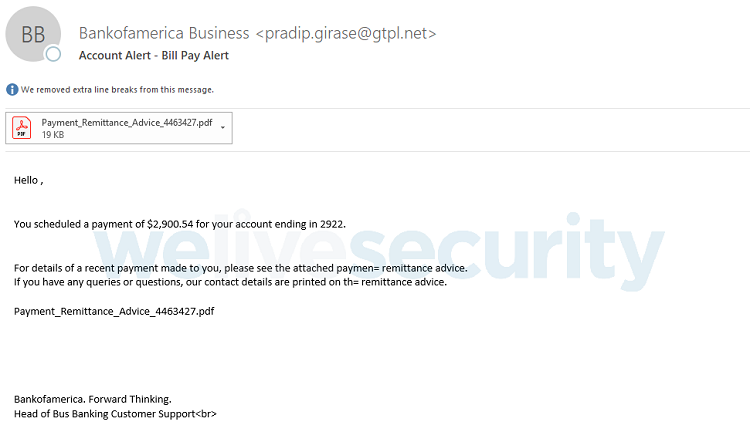
A new spam campaign is spreading the Emotet malware to unsuspecting victims via email, ESET Research discovered in November.

The well-known Emotet malware has recently been updated with a new email scraping module to collect emails from infected systems, security researchers at Kryptos Logi have observed.
Emotet malware can also steal proprietary information, credentials , and personally identifiable information (PII), which are a leading cause of identity theft.
Additionally, Emotet is also known to be used as a dropper or downloader for other potentially more harmful subsequent malware programs.
As reported by ESET Research, the Emotet spam campaign circulating since November spreads the malware using emails containing malicious attachments that are either invoices, bank account notifications or payment notifications or hyperlinks to domains controlled by the crooks behind the Trojan as an alternative starting point for infection.
The process starts automatically from the moment the victim opens the malicious attachments and activates the infection mechanism (Word macros or PDF), Emotet is downloaded, installed and launched on the system.
The malware then reports the successful infection to the command-and-control (C&C) server, which sends detailed instructions regarding the modules and payloads that need to be "downloaded.".
Depending on the additional modules it installs on the victim's computer, Emotet will then be able to perform a wide range of tasks from self-promotion over the network and collecting sensitive information through ports.
Emotet's secondary payloads are IcedID, which links advanced browser manipulation tactics, and Trickbot, a highly adaptable information-stealing botnet that uses exposed IP cameras and routers as C&C servers.
Due to the actors behind it all, the Emotet malware was able to deploy new modules to the botnet at any time using the C&C servers, and even modules infected with older versions of the malware are not safe.
This is especially true given that Emotet masters are known to slow down botnet activity and use it in large spam campaigns like the one recently detected by ESET Research.