

In the last 24 hours, there has been a worldwide increase in attacks by hackers and cybercriminals on over 10,000 systems using the MongoDB database.

Once cybercriminals gain access to the databases, they perform a complete deletion and leave a note informing their victim that in order to restore the database to its previous state, they must pay between $150 and $500, depending on the case.
Security researchers who conducted a statistical analysis of the attacks concluded that about 25% of Internet-accessible Mongo databases. The attack is happening because administrators leave their database Administrator accounts passwordless! -SHIT- (password less).
The SecNews research team has been conducting a thorough investigation and recording of exposed MongoDB databases in Greek cyberspace for 6 days. The findings will amaze you!
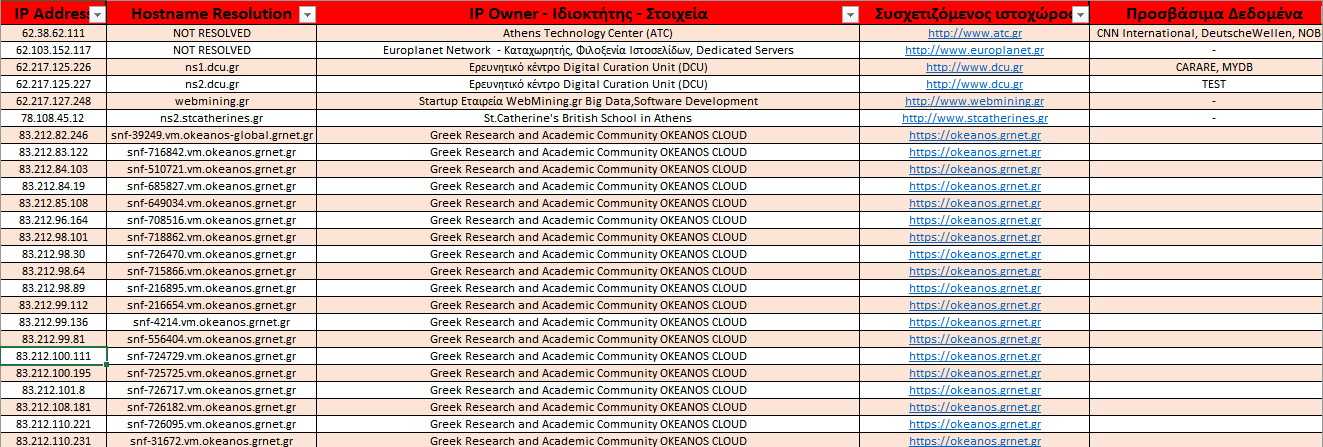
As we found out, among the exposed databases there are:
- Data from Twitter user monitoring applications, for reasons we do not know, from research institutions and institutes that focus on social media monitoring.
- Data on percentages of Greek parties in elections that have been made available to research institutions (universities)
- Gas station input/output system
- Citizen data in an electricity company database
- A large amount of data of unknown significance, exposed in the GRNET (University Network) Cloud service
- Data from Research Centers, Technology Institutes and Universities
- Data of Hosting companies or their customers
- Other Company Data
...and many more that we have not yet had time to investigate/identify!
We decided to publish the research findings here:
You can add comments to the document we are publishing with more information regarding additional findings, as well as make your own reports if you identify something extremely important, and most importantly, DO inform the system administrators so that they can be protected!
As we found during our research, anyone with a low level of technical expertise, using the Robomongo tool in combination with Kali Linux & the NOSQL Exploitation Framework, can extract data from the above databases - often sensitive data - with extreme ease!
The reasons for the disclosure are primarily the protection of critical infrastructure in Greece from the attacks of recent days on MongoDB databases. In addition, we are disclosing the above findings to protect society as a whole and the infrastructure of companies that may have exposed customer or citizen data on the internet.
Any system administrators or companies who recognize their unique IP addresses in the table we are publishing should IMMEDIATELY implement the instructions announced by the MongoDB vendor here:
https://www.mongodb.com/blog/post/how-to-avoid-a-malicious-attack-that-ransoms-your-data
In any other case, they put their customers' or companies' data at IMMEDIATE risk in the coming days or hours.
Update 1 – [10/1/2017 – 00:38]: Many of the aforementioned databases have already fallen victim to the Ransomware we are mentioning. We have just been informed of cases in Greece, with administrators having to pay significant amounts of money to restore their data!
Update 2 – [10/1/2017 – 01:2o] Information about the cybercriminals who have been encrypting MongoDB databases in recent hours can be found at the link [here] so that you know all the information available about them.
