

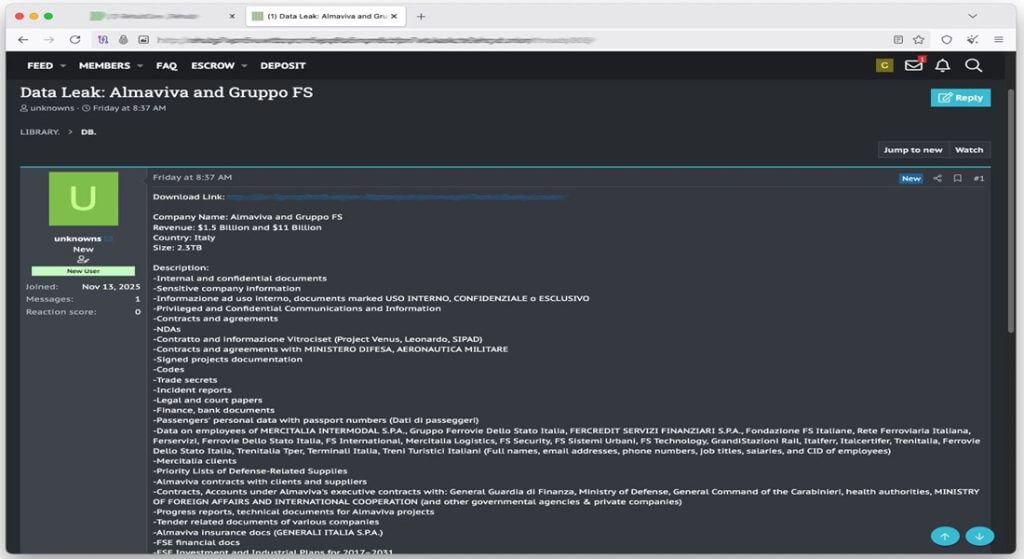
One of the biggest cyberattacks recorded in Italy appears to be affecting the public railway operator FS Italiane Group. The organization's data was exposed after Almaviva, the main IT provider supporting the group's systems, was breached. The attacker, who posted the leak on a well-known dark web forum, claims to have obtained 2.3 terabytes of sensitive company files.
What does the leak involve?
According to the hacker's post, the material includes confidential documents, internal communications, technical documentation and data from multiple subsidiaries of the FS group. The contents of the leak are described as "integrated company repositories", along with contracts with public bodies, accounting records, personnel files and project deliverables.
See also: MuddyWater uses hacked CCTV cameras to guide missiles
Andrea Draghetti, head of Cyber Threat Intelligence at D3Lab, said the files are recent, dating back to the third quarter of 2025. This rules out the possibility that this is older material from the Hive ransomware attack in 2022 — a case that had caused major problems but is now considered “closed.”
Draghetti also noted that the structure of the leak, organized into individual compressed folders by department and company, is typical of the tactics followed by ransomware groups and data brokers in recent years.
Who is Almaviva and how big is the blow?
Almaviva is one of Italy's largest technology providers, with more than 41,000 employees in nearly 80 branches. The company provides CRM systems, software development services and IT consulting to a large number of public and private organizations — making any breach highly critical.
At the same time, the FS Italiane group is one of the largest industrial players in the country, fully state-owned, with annual revenues of over $18 billion. It manages everything from rail infrastructure to passenger and freight transport, while also expanding into logistics and bus services. The extent of its activities makes any data leak particularly dangerous, both operationally and geopolitically.
See also: TamperedChef: Malware distribution via fake installers
Almaviva's official reaction
After days of silence, Almaviva confirmed the incident in statements to Italian media. It said: “ Security monitoring services have detected and isolated a cyberattack that affected our corporate systems, resulting in the theft of certain data .” The company added that it had immediately activated incident response procedures , ensuring the functionality of critical services, and had informed the relevant authorities — from the police and the national cybersecurity agency to the data protection authority.
The investigation is ongoing and continues in collaboration with government agencies, while Almaviva states that it will publish updates with full transparency.
Unknown if passenger data is affected
It is not yet clear whether the stolen files include personal data of Italian railway passengers or information that could compromise transport safety, but the breadth of the files — from HR to accounting — leaves open the possibility of significant consequences.
At the same time, it is unclear whether the breach affects other Almaviva customers outside the FS group.

Another sign of the broader cybersecurity crisis
The incident adds to a series of powerful attacks that have targeted critical infrastructure and large IT providers since 2024. The dependence of large government organizations on external partners creates additional levels of risk, as the security chain often breaks at its weakest point.
See also: PlushDaemon hackers compromise software updates for cyber espionage
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
In light of this, experts are urging stricter control of third-party vendors, enhanced access monitoring , and faster implementation of zero-trust architectures — practices now considered essential for organizations of high strategic importance like FS Italiane Group.
Source: www.bleepingcomputer.com
