

Lake Charles Memorial Health System (LCMHS) in Louisiana is informing through alerts about a data breach (following a ransomware attack) affecting nearly 270,000 patients who have received care at one of its medical centers.
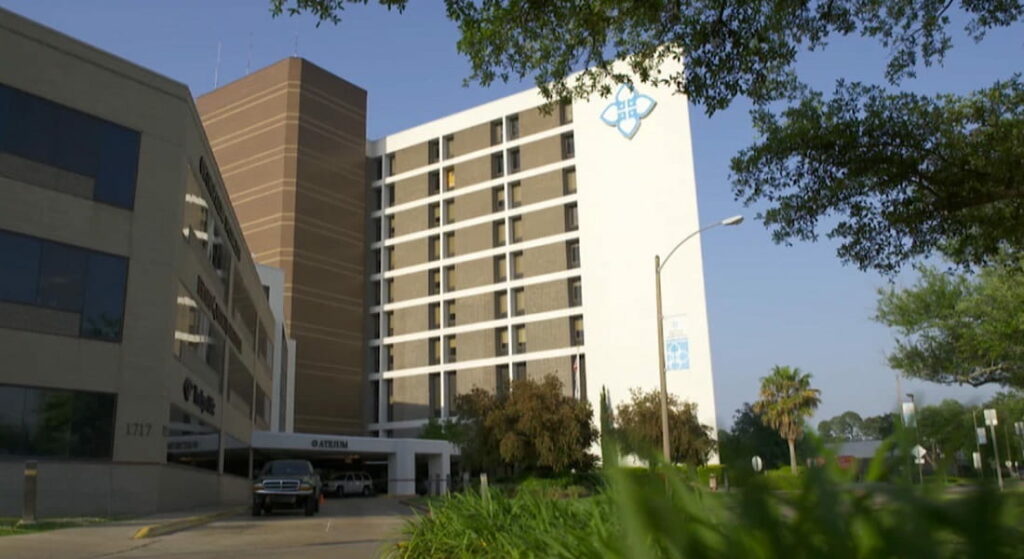
As the largest healthcare facility in Lake Charles, Louisiana, LCMHS is a hub of medical services. The complex includes 314 hospital beds, 54 beds dedicated to women's health care needs, and 42 beds dedicated exclusively to behavioral health issues. There is also a clinic that offers primary care to those without insurance.
See also: Americans lost $10 billion to scam call centers in India
On October 21, 2022, the LCMHS security team detected suspicious activity on its computer network. The healthcare provider posted an announcement regarding the matter on its official website.
After a comprehensive internal investigation, it was determined that malicious actors successfully breached LCMHS's system and stole confidential data.
This patient data included:
- Full name
- Home address
- Dates of birth
- Medical records
- Patient identification numbers
- Health insurance information
- Payment Information
- Limited clinical information about the care received
- Social Security Numbers (in some cases)
LCMHS confirmed that their digital medical records remained secure.
“As of December 23, 2022, we are sending letters to patients whose information may be involved in this incident,” the announcement states.

“ We offer free credit monitoring and identity theft protection services to individuals whose Social Security numbers may have been compromised. Patients are encouraged to check their health and healthcare providers’ statements and contact them immediately if they see services they did not receive insurer ,” LCMHS states
See also: BTC.com hacked: Hackers stole $3 million worth of crypto
LCMHS in Louisiana notified the U.S. Department of Health and Human Services (HHS) about the incident, which has now affected a total of 269,752 people according to the HHS portal related to health sector breaches.
Hive ransomware gang claims responsibility for attack
On November 15, 2022, the Hive ransomware group listed LCMHS on its data leak website . Attackers usually reach this point when negotiations for a ransom payment are unsuccessful.
Surprisingly, the hackers said the encryption took place on October 25th – four days after LCMHS first noticed that its network had been compromised.
Hive published the files allegedly stolen after the LCMHS systems were breached
According to BleepingComputer, among the files listed are bills of materials, cards, contracts, medical information, documents, etc. However, we still don't know if these files are actually real.
The FBI and other government authorities issued a warning that since November, Hive ransomware had been used to extort more than 1,300 companies around the world, the majority of which were in the healthcare industry.
See also: North Korean hackers target South Korean foreign policy experts
Patients who have received medical care at LCMHS in Louisiana should be very careful with messages and emails they receive, especially if they ask for personal information.

Ransomware is becoming an increasingly serious issue for healthcare organizations around the world. By investing in strong cybersecurity measures, training staff on best practices, and responding quickly in the event of an attack, healthcare organizations can minimize risk and protect their valuable data from malicious actors online. The growing threat of ransomware in healthcare means that taking proactive measures will go a long way in keeping patient information secure in the future.
Source: www.bleepingcomputer.com
