


Security researchers have discovered a new Mac malware that spreads via infected Google search results . The malware appears as an Adobe Flash Player installer (.DMG disk image).
According to VirusTotal, the malware installer and its payload were not detected by virus detection engines.
Mac Malware Shlayer
Security researchers at Intego have spotted this new version of Shlayer Mac malware that is distributed as a Trojan horse file (.DMG disk image) and disguised as Adobe Flash Player.
Once the user installs the malicious Adobe Flash Player on their Mac machine, some instructions will appear.
“The instructions tell users to ‘right-click’ the Flash installer, select ‘Open’, and then click ‘Open’ in the window that appears,” Intego researchers said in a post
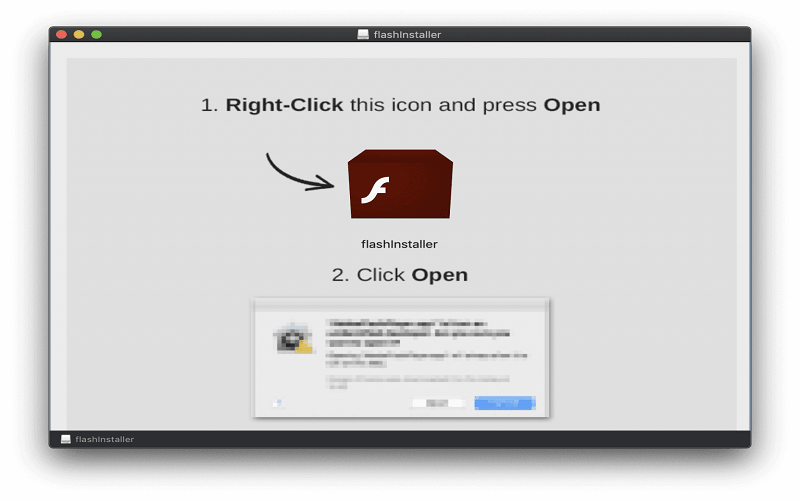
When the user starts following the instructions to install the malicious application, the icon looks like the Flash player, but other processes are happening in the background.
A bash script is used, which extracts a password-protected .zip archive file and secretly stores the malicious application in a temporary folder.
The Mac malware also downloads Adobe's legitimate Flash Player installer to trick the user, but it also downloads other malicious applications.
“The developers’ decision to hide the Mac .app in a protected .zip file, and that file inside a bash shell script, is a novel idea – and it’s also extremely clear that the developers are trying to avoid detection by antivirus software.”
“This newly modified Mac malware purports to be a legitimate Flash Player installer, but in reality it can secretly download and install unwanted packages containing adware or spyware.”
Shlayer Mac malware is believed to be one of the largest and most widespread threats to macOS. In February, researchers at Carbon Black discovered a new Shlayer malware that targeted versions 10.10.5 to 10.14.3.
Adobe has already announced that it will stop distributing and updating Flash Player after December 31, 2020..
