

On December 13, New Orleans was hit by a ransomware attack . According to some files uploaded to the scanning service VirusTotal , it is likely the Ryuk Ransomware .
On December 14, 2019, someone (with an American IP address) uploaded memory dumps of suspicious executables to the VirusTotal service.
One of these memory dumps contained numerous references to New Orleans and Ryuk.
Memory dumps show the memory used by a running application. Therefore, they are very useful because they allow the extraction of useful strings, file names, commands, and other information, with which the executable interacted. For this reason, they are often used by experts to investigate hacking attacks.
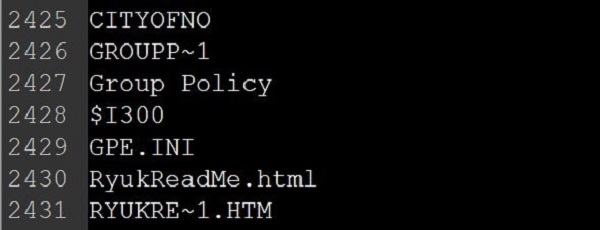
The memory dump refers to an executable file called 'yoletby.exe' and contains numerous references to New Orleans, such as domain names, domain controllers, internal IP addresses, usernames ,shared files, and references to the Ryuk ransomware.
Other information included in the dump was the HERMES file marker, filenames ending with the .ryk extension, and references to RyukReadMe.html ransom.
A reference to the executable file C:\Temp\v2.exe was also found , which was executed on the machine. A memory dump for this file was also uploaded to VirusTotal .
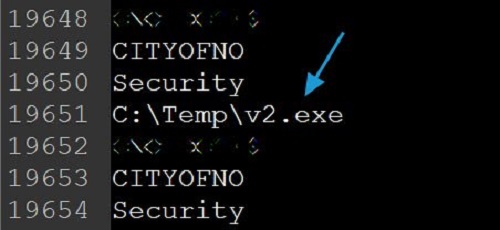
There were references to the New Orleans City Hall there.
Further analysis of the evidence showed that the Ryuk ransomware was most likely behind the attack .
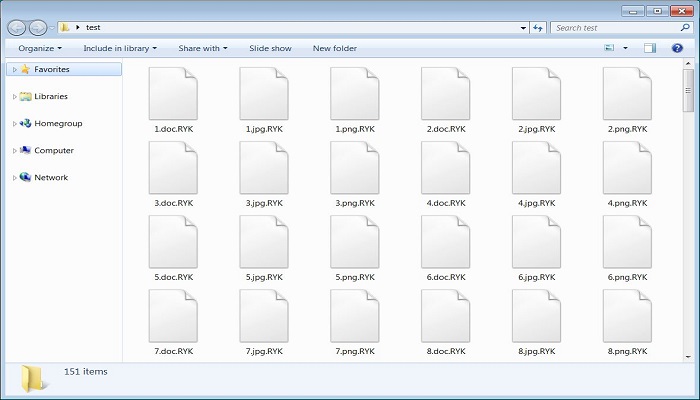
If this is true, then New Orleans is another victim of the popular ransomware.
Possible presence of Emotet and Trickbot
If New Orleans was indeed attacked by Ryuk ransomware, then the network may also have been infected by Emotet and TrickBot.
Emotet is usually distributed via spam emails, which contain malicious attachments.
After the system is infected by Emotet, the malware will send spam emails to other computers and download other malicious programs to the computer.
One of the most common malware installed by Emotet is TrickBot, which is used to steal information.
