

Lenovo has confirmed that its Fingerprint Manager Pro (version 8.01.86) auto-login software, which allows users to unlock their devices using fingerprint recognition, is affected by a serious vulnerability.
Attackers could exploit the vulnerability to gain access to any system equipped with the application.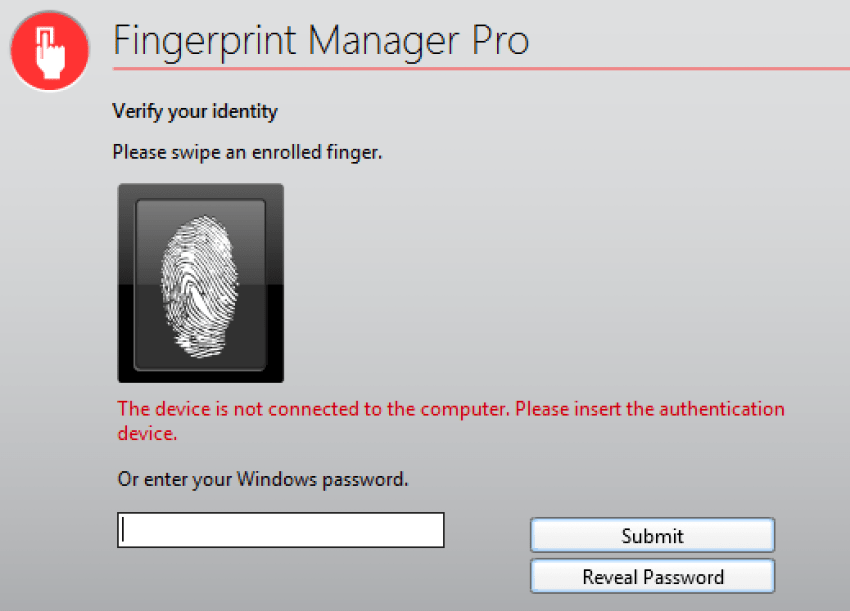
According to Lenovo’s disclosure, Fingerprint Manager contained a hardcoded password that could allow users to log in locally to accounts without administrator privileges.
In addition to the hardcoded password, the “security” application stored sensitive information such as Windows logon credentials and fingerprints, which it “encrypted using a weak algorithm.”
The vulnerability was discovered by researcher Jackson Thuraisamy of Security Compass.
https://www.youtube.com/watch?v=JRA34PzvANg
The flawed software is available for Windows 7, 8, and 8.1. According to the details published on the company's website, below are all the devices that use Fingerprint Manager:
- ThinkPad L560
- ThinkPad P40 Yoga, P50s
- ThinkPad T440, T440p, T440s, T450, T450s, T460, T540p, T550, T560
- ThinkPad W540, W541, W550s
- ThinkPad X1 Carbon (Type 20A7, 20A8), X1 Carbon (Type 20BS, 20BT)
- ThinkPad X240, X240s, X250, X260
- ThinkPad Yoga 14 (20FY), Yoga 460
- ThinkCentre M73, M73z, M78, M79, M83, M93, M93p, M93z
- ThinkStation E32, P300, P500, P700, P900
Those of you who have any of the above devices, and the version of Fingerprint Manager Pro is 8.01.86, are recommended to immediately update to version 8.01.87 or a later version. You can do so from the following link:
https://pcsupport.lenovο.com/downloads/ds034486
Information, header image: TNW
