

A file containing 1.4 billion passwords, which have not been encrypted (or have been decrypted - clear text) are circulating on the Dark Web.
The file contains over 1.4 billion email addresses, passwords and other credentials, all in clear text, and was discovered by security firm 4iQ.
The 41 gigabyte file was discovered on December 5. It was updated late last month, indicating that the data is current and being used by third parties. The identity of the hacker who posted it is unknown, but he left details of any donations in Bitcoin and Dogecoin.
“None of the passwords are encrypted, and what’s scary is that we tested some of them and most of them work,” said Julio Casal, founder of 4iQ. “The breach is almost double the size of the previous largest leak, the list from Exploit.in that exposed 797 million records.”
The Exploit.in list is included in this dump, as are files that have been reported stolen before. However, much of the data appears to be completely new.
See the images uploaded by medium.com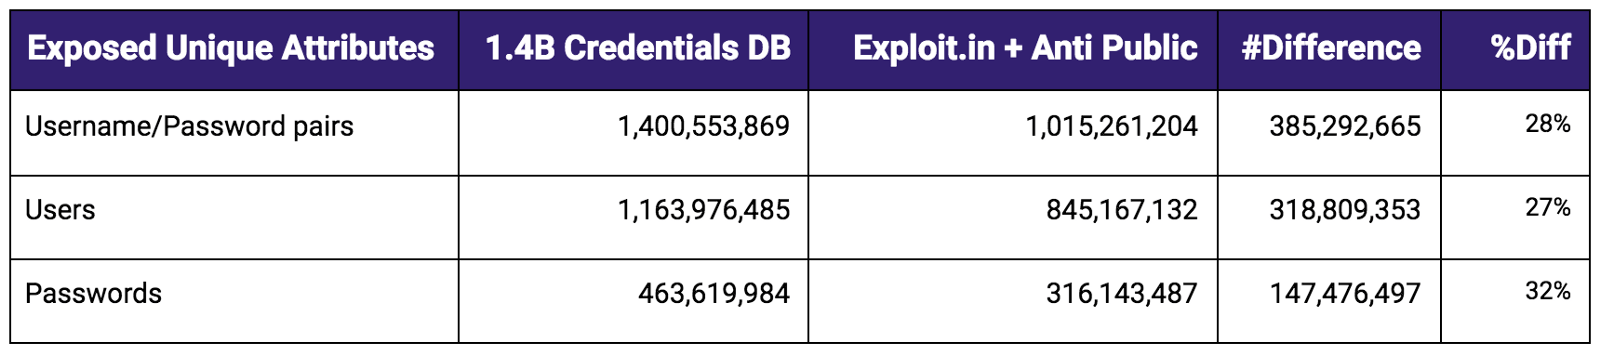

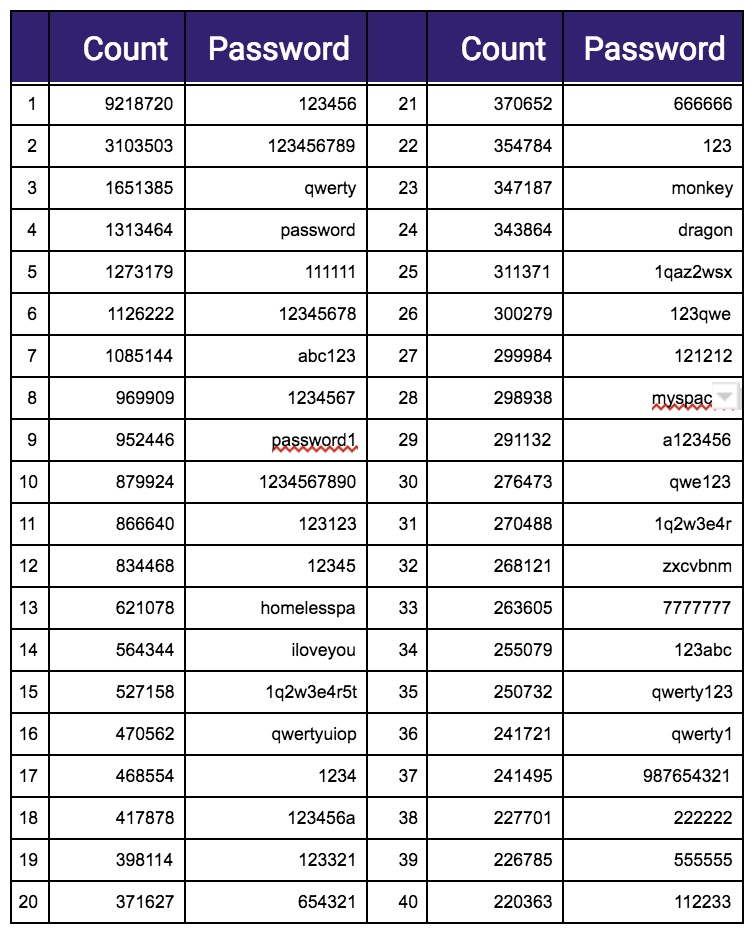
The security company attempted to contact some of those registered on the list, and the email addresses of many turned out to be active, although in most cases the passwords were no longer in use.
But no matter how we do it, the size of the leak is a treasure trove for hackers, as all these passwords together constitute a first-class library for brute force attacks..
