

Tools built into Mac computers designed to protect users from malicious content can be easily bypassed, according to a security researcher.
Speaking at the RSA conference in San Francisco on Thursday, SYNACK research director Patrick Wardle described how two security tools used in OS X can be bypassed to run malware.
Wardle, according to ZDNet, said: “If Macs were completely secure, I wouldn’t be here talking.”
The two security features, Gatekeeper and XProtect, were added to the latest versions of OS X in response to the growing threats from malware.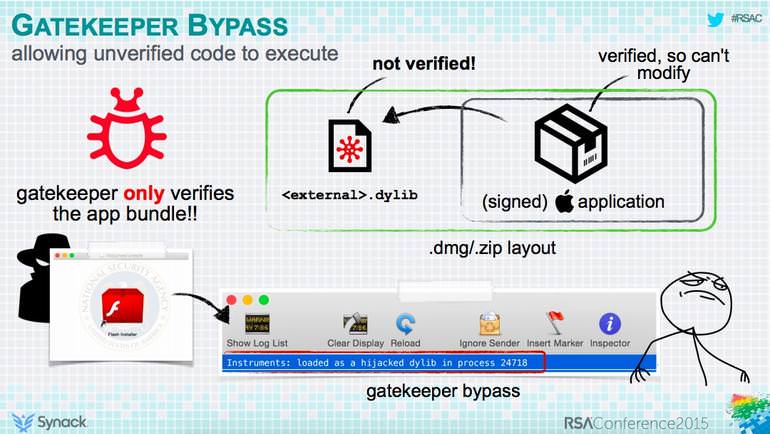
Gatekeeper, added in OS X 10.8 “Mountain Lion,” restricts how applications can open and run on a computer. Most applications are set to be verified through Apple’s App Store, or by trusted developers. XProtect, a rudimentary malware scanner for Macs, was added in OS X 10.6 “Snow Leopard.” It can also block specific applications and plugins if they have known vulnerabilities.
“Gatekeeper doesn’t verify the content of apps,” Wardle said. When an app goes to run, Gatekeeper either knows where it’s from and allows it to run, or it doesn’t and doesn’t let the app run. It doesn’t constantly check the app, which Wardle said could be a problem.
“So if I can find an Apple-approved app and modify it to load external content, when the user runs it, Gatekeeper can be bypassed.”
He also stated that XProtect was very easy to bypass.
A recompilation of a known malware sample can change its hash, and so Wardle was able to sneak malware under XProtect's nose.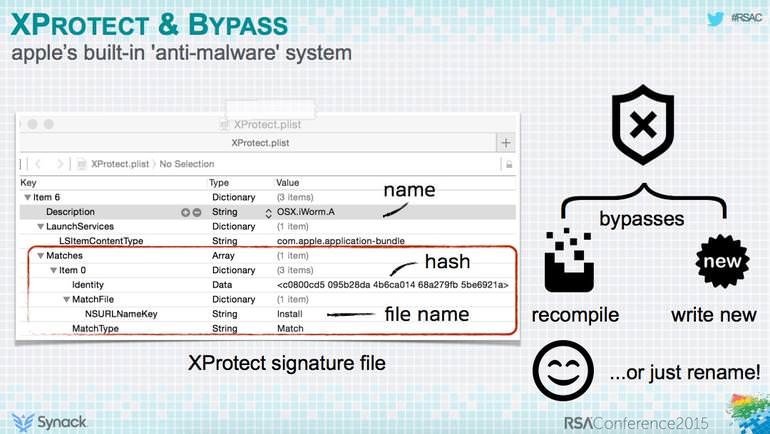
Additionally, although he called XProtect's sandboxing feature "powerful," it can still be bypassed with a number of known kernel-level vulnerabilities.
