

A Chinese hacking group has been allegedly spying on governments for over a decade, according to FireEye. The APT30 hacking group was exposed by security firm FireEye, which claims to have been spying on governments in Asia and the Pacific since 2004.
FireEye states in its report that the APT30 has a particular interest in political developments in Southeast Asia and India, and is particularly active at the time of Southeast Asian summits. 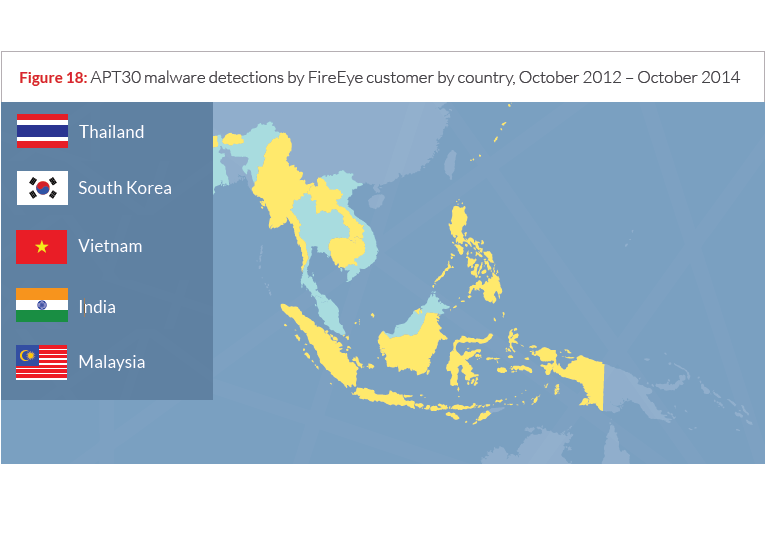
It also focuses on regional issues and territorial disputes between China, India, and Southeast Asian countries.
FireEye's report, APT30 and the Mechanics of a Long-Running Cyber Espionage Operation (PDF), states that the group has consistently focused on Southeast Asia and India over the past 10 years.
In addition to Asian governments, APT30 also targets media companies and journalists who report on issues concerning the region.
“We have analyzed over 200 malware samples as well as the remote controller software that uses a GUI, and we are able to assess that it was developed by the APT 30 group,” FireEye says.
“All of their hacks focus on obtaining sensitive data from multiple targets, potentially using government networks and other networks that are inaccessible from a typical internet connection.”
“The bulk of APT30’s efforts use social engineering and show a particular interest in regional politics, military and economic issues, disputed territories, media companies and journalists who denounce issues concerning China and government legitimacy,” the FireEye report says, pointing to China as behind the group.
The security firm's white paper also states that, while attribution of responsibility is always difficult, evidence suggests that the APT30 group may be funded by Chinese authorities.
“Such prolonged, planned efforts to develop new tools, combined with the group’s regional goals and missions, lead us to believe that their activities are state-sponsored, most likely by the Chinese government,” the report states.
The group allegedly infects its victims with phishing messages, and uses sophisticated attack tools that have been developed over the past 10 years.
FireEye said that some of the malware used by APT 30, most notably Backspace and Flashflood – are used to infect systems and steal data over the air. What’s striking is that these malicious tools appear to have been designed when they began their efforts in 2005.
