The Anatomy of a Web App Attack: How Does It Happen? What are its 5 Stages?
If we start taking a look at the hacking attacks that took place in 2015 alone, we will easily notice that the number of personal data compromised or leaked is approaching one billion. In 2015, we saw some of the most notorious hacking attacks to date, attacks such as those carried out on Ashleey Madison, TalkTalk, Patreon Donation Site, the Pentagon, etc.
As application development increasingly permeates the internet, the World Wide Web is home to everything we need. In 2015, we also saw an increase in Web App Attacks carried out using a well-designed plan-of-action.
https://www.secnews.gr/100393/the-most-secure-mobile-platform/Can you guess which is the most secure mobile OS? You'll be surprised!
The attack usually targets the web server used by the target company. Despite network defenses, such as intrusion penetration systems and firewalls, the web application could be attacked by a malicious actor in a variety of ways.
So what is a Web App Attack? And how does it work?
In this article, we will explain the five stages of a Web App Attack from a hacker's perspective. Each stage will be explained in three parts –
1. What is it?
2. How does it work? And
3. How can I defend myself against it?
The five stages that will be analyzed below are:
– Reconnaissance,
– Scanning,
– Gaining Access,
– Maintaining Access, and
– Covering Tracks.
https://www.secnews.gr/99718/reverse-atm-attack-used-to-steal-nearly-4-million-in-cash/btn-large” variation=”btn-info”]See also: Do you know what a reverse ATM attack is? It's time to find out!
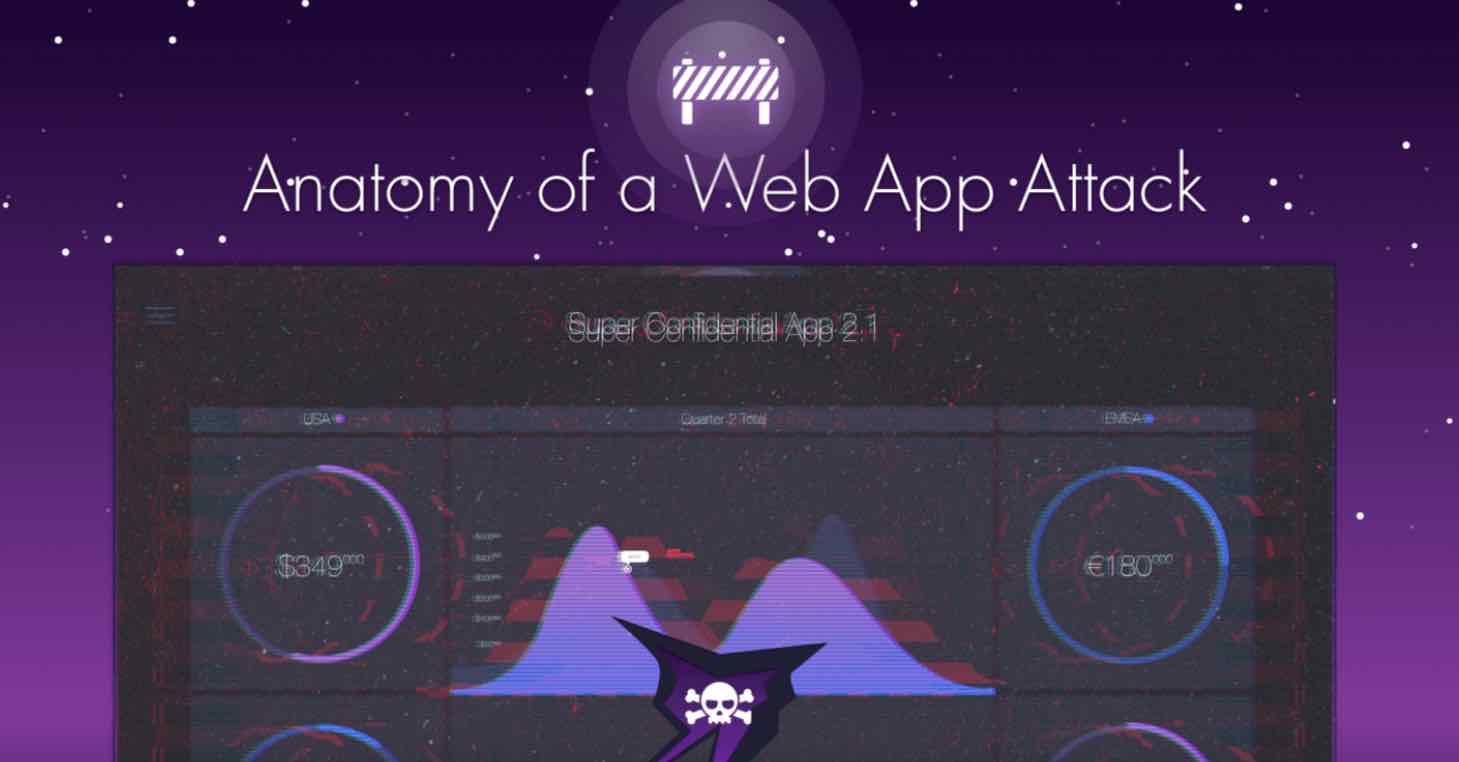
And since a picture is worth a thousand words, let's pay close attention and observe this extremely interesting infographic from Barricade.