

Active attack on Eurobank customers: On Sunday, August 9, 2026, a new Eurobank phishing has begun — dozens of customers have received a fake SMS claiming that they have 9,428 points ready to expire and redirecting them to a fake redemption website. The website, hosted on the domain eurobanktes.vip, is a replica of the official Eurobank and its purpose is to steal e-Banking and credit card details. The SecNews technical team recorded the attack as it unfolded, identified the infrastructure hosting it and warns all bank customers not to follow the link.
See also: iPhone 18 pre-order scams: How to avoid falling for phishing

The exact message being circulated
The SMS arrives from a spoofed number +3069776406576, which in itself is a red flag — it has 11 digits after the country code while Greek mobiles always have 10 digits. The exact text is:
"Expiration Reminder: Your 9428 EUROBANK points are about to expire. Visit the official website immediately to redeem them for cash: https://eurobanktes.vip/gr"
The message exploits three classic social engineering techniques: urgency (“they’re about to expire”), tangible benefit (“redeemed with cash”), and direct action (“visit now”). It doesn’t mention the recipient’s name, which always gives away a mass mailing.
What does the fake website look like?
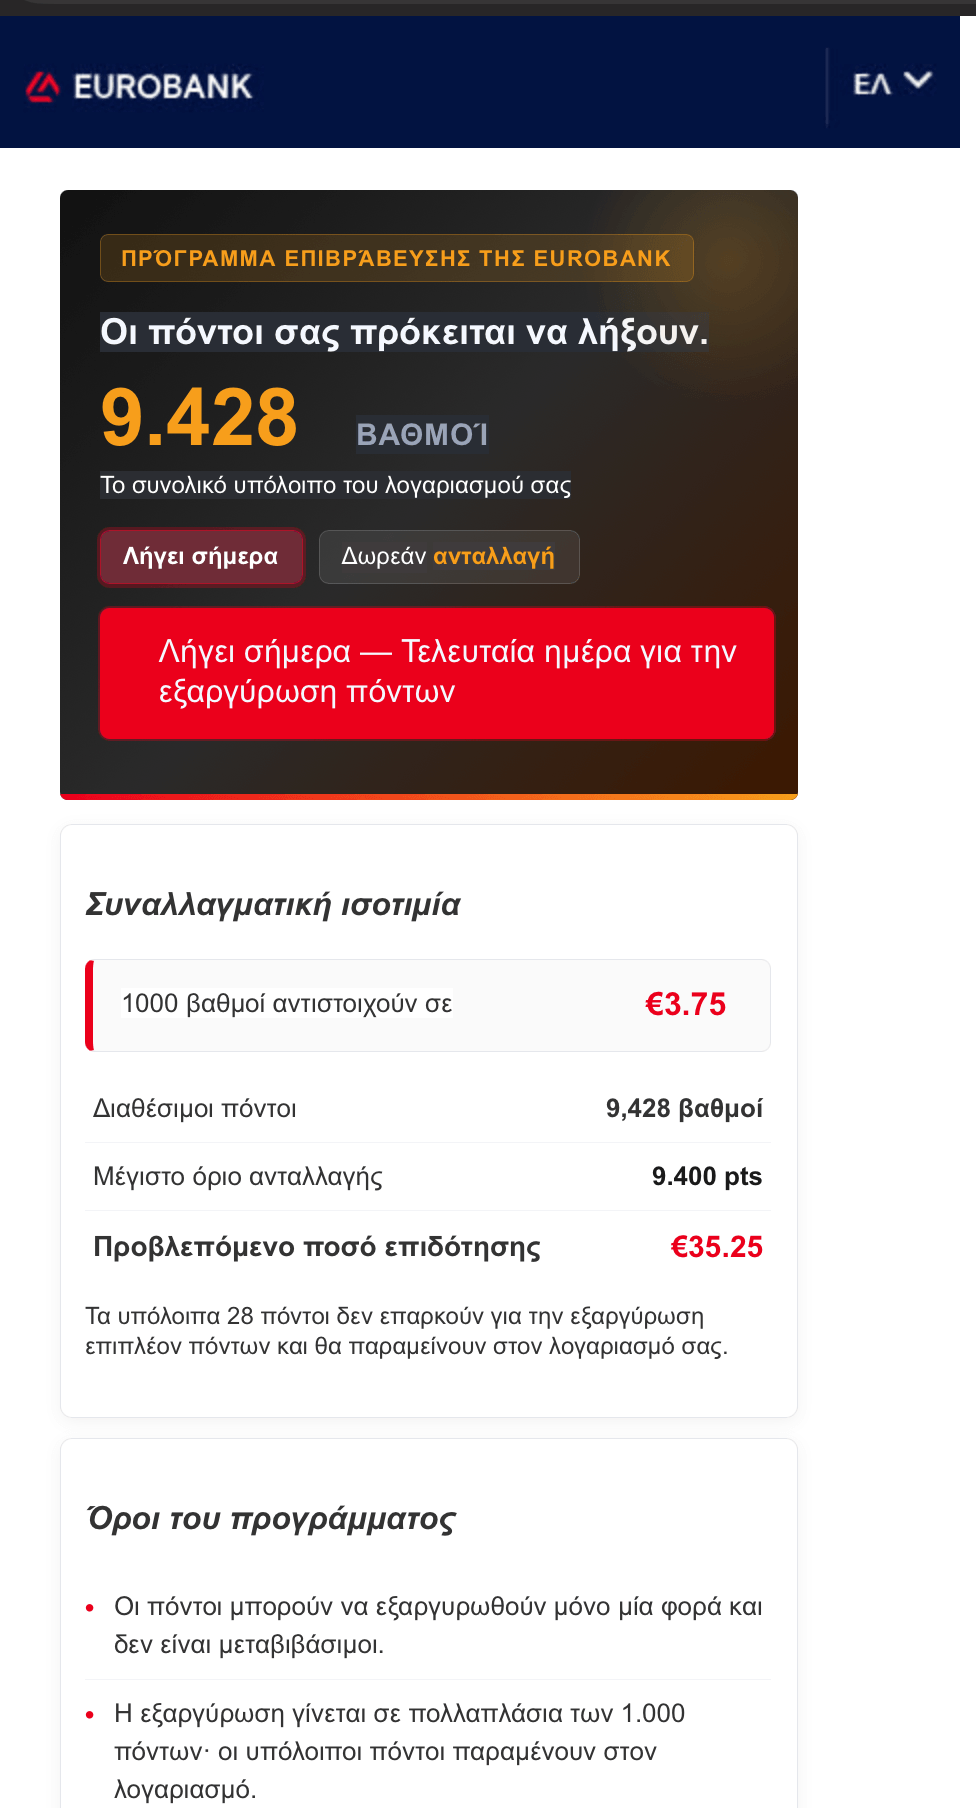
The SecNews technical team has visited the domain in a controlled, isolated environment. The page displays:
- Eurobank logo and colors faithfully reproduced
- Indication "EUROBANK REWARDS PROGRAM" with the exact amount of 9,428 points
- False indication "Expires today — Last day to redeem points"
- Realistic bait: "1000 points correspond to €3.75", with a projected subsidy of €35.25 for the 9,400 redeemable points
- Full set of program terms to give validity to the process
- Select language EL — to match the targeted Greek users
In the next steps, the page requests e-Banking credentials and card details for a supposed “cash deposit.” This is where the attack is complete — the details are sent to the attackers and the accounts are emptied within hours.
Technical analysis of the infrastructure
- Domain:
eurobanktes.vip - TLD:
.vip— extension systematically exploited for banking and crypto fraud due to low cost and minimal control - Front-end IP: 104.21.16.214 and 172.67.215.243 — both belong to Cloudflare, used as a proxy to hide the real origin server
- Nameservers:
courtney.ns.cloudflare.com,jihoon.ns.cloudflare.com - Server header: Cloudflare, with SSL certificate that gives a false sense of security (the green padlock does not mean a legitimate page)
- Redirect behavior: /
grdoes an HTTP 307 redirect to/gr/, apparently to handle variations in the input - SMS Number: Spoofed or forged via SMS gateway — Greek mobiles follow the pattern
+30 6XX XXX XXXXwith exactly 10 digits after the +30 code
Using Cloudflare as a proxy does not mean that the company itself is involved — on the contrary, it is a common tactic by hackers to hide the true location of the server and make it difficult to take down.
Immediate measures you should take
- Do not click on the link. Even a simple visit can trigger a tracking pixel that confirms the number as active to the adversary.
- Delete the SMS. Do not reply or forward.
- If you opened it but didn't enter any data, no serious damage has occurred. Clear your browser cache and history to be safe.
- If you registered e-Banking credentials, call immediately at 800 111 1144 (Eurobank customer service, available 24/7) to block and change passwords.
- If you registered card details, cancel the card and check transactions immediately through the official app.
- If you have made a transaction, please also inform the Directorate for the Prosecution of Electronic Crime at 11188 or via
cyberkid.gov.gr
See also: iCloud Private Relay: A passkey request is enough to reveal the real IP
What should Eurobank do immediately?
Due to the massive nature of the attack and the technically convincing clone, the SecNews technical team calls on Eurobank to immediately activate the following measures:
- Public announcement on all channels — website, app, social media, SMS to all customers — with a precise description of the attack and the domain
- Takedown request to Cloudflare via Trust & Safety report with impersonation documentation
- Request for domain seizure to the
.vipregistrar , with legal documentation from the bank's legal department - Update from the Bank of Greece and the Association of Hellenic Banks on coordination between banks
- CSIRT.gr and the Cybercrime Prosecution Office informed about an official investigation
- Strengthening fraud monitoring in subsequent customer transactions, especially express transactions to new recipients
- Temporarily suspend or strengthen transaction confirmation from devices that have visited the domain — if possible through threat intelligence feeds
Why this Eurobank phishing campaign is dangerous
- Realistic number of points: 9,428 points is a number that suits a moderately active credit card holder — it's not blatantly fake like "You've won 1 million"
- Good Greek syntax: No obvious grammatical errors, with the correct spelling of "redemption"
- Free redemption simulation: The “Free exchange” option reduces suspicions about a charge
- Real SSL lock: Cloudflare provides free SSL, so the browser displays the green lock and gives a false sense of security
- Domain that "looks" like eurobank:
eurobanktes.vipat first glance looks almost official, especially on a small mobile screen
Also useful: Hackers Tracked Child via Kids' Smartwatch
What Eurobank never does
- Does not send SMS with a link to "redeem points"
- Does not send urgent messages about points "expiring" in 24 hours
- Does not request e-Banking codes via SMS or email
- Does not communicate from 11-digit mobile number
- It does not use domains other than
eurobank.gr,eurobankmb.grand official subdomains.
The eurobanktes.vip campaign is indicative of a broader trend of smishing against Greek bank customers. Similar attacks have been recorded from time to time on customers of other banks, with domains that always follow the same pattern: variation of the name + cheap suffix. The editorial team of SecNews will monitor the development of the attack, the possible official announcement by Eurobank, and the takedown of the domain. We ask readers who received the same or similar SMS to report it to their bank and to the Prosecution of Electronic Crime. Sources: Eurobank Security Center , CyberKid EL.AS. , Data Protection Authority .
🔑 Secure your passwords with Proton Pass
Password manager from Proton — end-to-end encryption, passkeys, built-in 2FA, and monitoring for leaks of your credentials.
- ✔ Encrypted storage of passwords & passkeys
- ✔ Notification if any of your passwords are leaked (Dark Web Monitoring)
- ✔ Free version — on all devices
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
