

A new variant of the ClickFix social engineering technique , known as InstallFix , has emerged and targets users who download and run command line interface (CLI) tools. Instead of using traditional phishing emails or malicious attachments, attackers convince users to run malicious commands by presenting them as legitimate CLI tool installation procedures.
The method exploits the common practice of developers executing scripts via curl-to-bash from online sources without carefully inspecting the code first. This approach makes even experienced users vulnerable, but becomes especially dangerous for non-technical users who are now working with tools that were previously reserved for developers.
See also: Mirax Bot: New Android malware advertised on hacking forum
Cloned pages and misleading instructions
Push Security , a company that specializes in detecting and remediating browser threats, discovered that attackers are creating clones of official installation pages for popular CLI tools , such as Anthropic's Claude Code . The cloned pages maintain the same layout, branding, and documentation as the legitimate ones, but the installation instructions for macOS and Windows lead to the execution of malware controlled by the attackers.
A feature of the scam is that the links outside the installation redirect to the legitimate website, creating a false sense of security. Thus, victims may follow the fake instructions without realizing that they are executing malicious commands.
Malicious campaigns via Google Ads
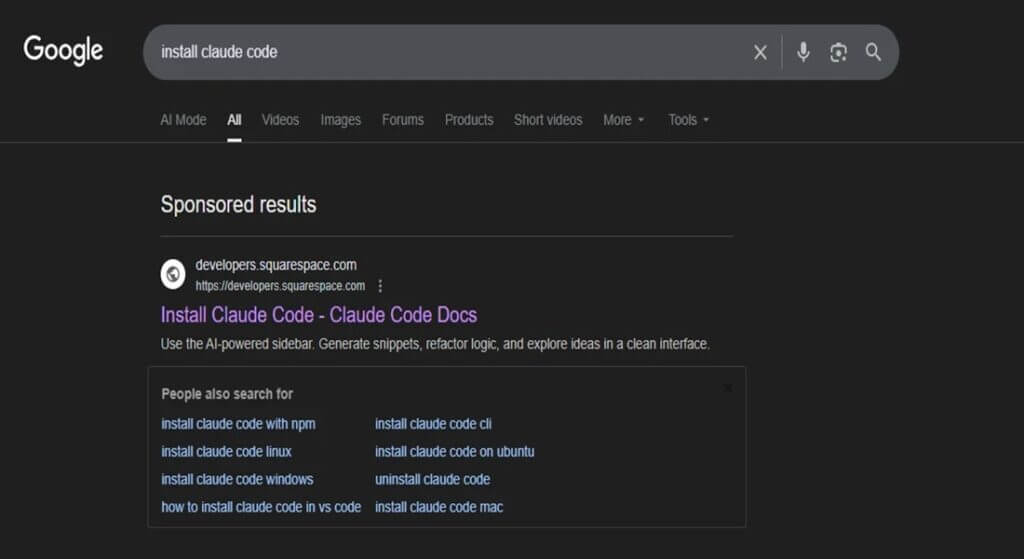
Attackers are promoting the fake pages through malicious campaigns Google Ads, causing the pages to appear as top results for searches such as “Claude Code install” or “Claude Code CLI.” BleepingComputer has confirmed that the malicious sites are still being displayed through search results, with one of the top results leading to a Squarespace that is a perfect clone of the official documentation.
See also: Microsoft: New ClickFix campaign distributes Lumma Stealer
Amatera: The malicious payload behind InstallFix
The InstallFix commands contain coded instructions to download and execute a binary. It activates mshta.exe to retrieve malicious content and conhost.exe to support execution. The final payload is the Amatera info-stealer, a new malware family believed to be based on ACR Stealer and sold as a service as a service (MaaS) to cybercriminals.
Amatera can collect passwords, cookies, session tokens from browsers, and system information, while avoiding detection by security tools. It is a highly targeted threat that leverages stealth execution techniques to bypass traditional protection measures.
Hosting platforms and detection challenges
One of the most worrying aspects is that malicious websites are hosted on legitimate platforms such as Cloudflare Pages, Squarespace, and Tencent EdgeOne, making them difficult to detect and block. Users may mistakenly trust the source due to the familiar domain and professional appearance of the page.
Recommendations for safe CLI tool download
Experts recommend that users download CLI tools only from official websites, bypass sponsored search results , and bookmark trusted download sources. Verifying the authenticity of the domain and carefully reading installation instructions before executing is crucial to avoiding infections.
See also: Dust Specter targets Iraqi officials with SPLITDROP and GHOSTFORM

Additionally, organizations and developers should implement security tools that monitor execution behaviors and educate users about the dangers of curl-to-bash and fake installation instructions.
With the increasing use of CLI tools by non-technical users, paying attention to the installation process and verifying sources is becoming a priority for cybersecurity.
🔑 Secure your passwords with Proton Pass
Password manager from Proton — end-to-end encryption, passkeys, built-in 2FA, and monitoring for leaks of your credentials.
- ✔ Encrypted storage of passwords & passkeys
- ✔ Notification if any of your passwords are leaked (Dark Web Monitoring)
- ✔ Free version — on all devices
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
Source: www.bleepingcomputer.com
