

The cybersecurity world was rocked last week by a massive leak of internal communications from the Black Basta ransomware group. The leak, which came from chat logs, is attributed to internal conflicts and retaliation following attacks on Russian banks. The leaked files offer a rare and valuable glimpse into the tactics, operations, and leadership structure of the notorious group.
See also: Were conversations of the Black Basta ransomware group leaked?
Understanding Black Basta’s attack tactics is crucial for businesses looking to strengthen their security. The Black Basta ransomware group exploits known vulnerabilities, misconfigurations, and inadequate security mechanisms to compromise systems. Their insider tactics reveal targeted attacks on exposed RDP servers, weak authentication systems, and the use of malicious dropper programs disguised as legitimate files.
The main attack vectors exploited by Black Basta ransomware include scanning for exposed RDP and VPN services. Attackers often rely on default or stolen VPN credentials to gain initial access, as well as exploiting known CVE vulnerabilities when systems remain unpatched. Malicious MSI and VBS-based droppers are commonly used to deliver malicious payloads, while Rundll32.exe is used to execute malicious DLLs. Additionally, credential harvesting and privilege escalation are key components of these tactics.
See also: Black Basta abuses Teams Chat to spread malware
The Black Basta Ransomware gangs remain relentless, and recent leaked conversations reveal their strategic plan: a list of targets that exploit vulnerabilities to infiltrate corporate networks. For IT security professionals, this list is not just a set of data — it is a call to immediate action.
Security teams must immediately address the above vulnerabilities, which are actively exploited in ransomware attacks.
Below is a handy table of the 20 most critical CVEs that require your immediate attention. These are vulnerabilities targeted by ransomware groups that, if not addressed immediately, could put your organization at serious risk. Qualys covers not only these, but also the 62 CVEs included in the leaked documents.
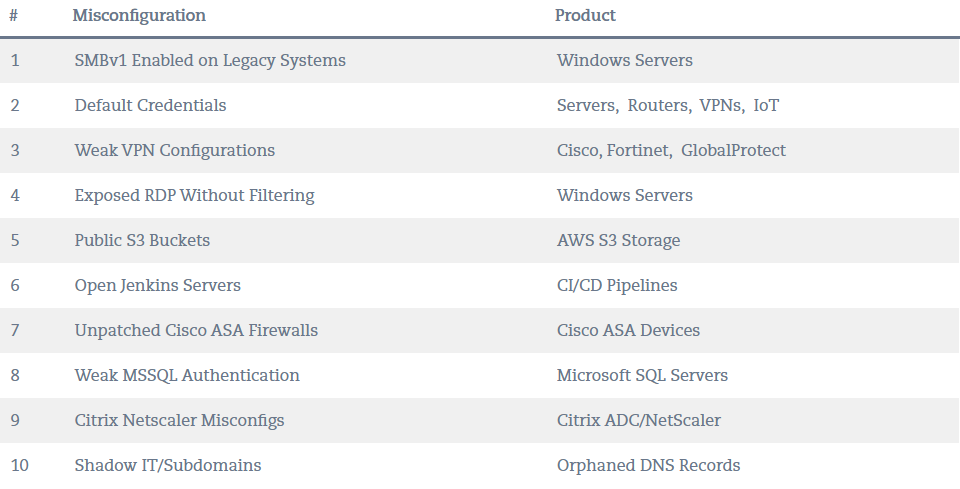
Black Basta employs a multi-pronged strategy, combining techniques such as credential theft, service exploitation (such as brute force attacks on RDP), social engineering , and access persistence. Credentials are acquired through phishing, supply chain breaches, dark web purchases, or identifying exposed services with tools such as Shodan and Fofa (automated scanners). They then brute force attacks on vulnerable login gateways, such as RDP, to gain access.
See also: Black Basta ransomware: All the new tactics it uses
The recent leak of internal chat logs from the Black Basta ransomware group revealed valuable and unprecedented insights into its operations, tools, and tactics. Qualys’ product suite is ideally suited to address the critical recommendations that have emerged, offering a comprehensive and unified approach to cybersecurity.
The CyberSecurity Asset Management (CSAM) solution offers comprehensive visibility into all assets, fully meeting the requirements for complete and accurate discovery. Qualys Patch Management is an advanced, automated solution that ensures timely and effective software updates. At the same time, Qualys VMDR facilitates the process of discovering, assessing and prioritizing vulnerabilities. Using TruRisk scoring , the platform enhances vulnerability management , offering risk-based prioritization and leading to more efficient and targeted cybersecurity measures.
Source: blog.qualys
☁️ Keep safe copies with Proton Drive
Encrypted cloud storage from Proton — protect your files from ransomware, corruption, and data loss with end-to-end encryption.
- ✔ End-to-end encrypted files & backups
- ✔ Version history — recover files after ransomware
- ✔ Free space — sync across all devices
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
