

Researchers have revealed the inner workings of Wizard Spider, a hacking group. On Wednesday, PRODAFT published the results of an investigation into the Wizard Spider group, which is believed to be either related to or affiliated with the Grim Spider and Lunar Spider hacking groups.
See also: Who are the top ten early access attack vectors?

According to the cybersecurity firm, the Wizard Spider group, likely of Russian origin, operates an infrastructure consisting of a “complex set of subgroups and teams, [..] has vast numbers of compromised devices under its command, and employs a “highly distributed professional workflow” to maintain security and a high operational tempo.”
Today’s most sophisticated cybercriminal enterprises, whether for pure profit or state interests — as is the case with many advanced persistent threat (APT) groups — often operate with business models. This includes recruiting top talent and creating an economic framework for depositing, transferring, and laundering proceeds.
See also: NVIDIA patches ten vulnerabilities in Windows GPU display drivers
In the case of the Wizard Spider team, that means it will be putting some of its profits back into development by investing in tools and software and paying for new hires. The report suggests that the team has “hundreds of millions of dollars in assets.”
PRODAFT says the Wizard Spider group focuses on breaching corporate networks and “has a significant presence in almost every developed country in the world, as well as many emerging economies.”
Victims include defense contractors, enterprise businesses, supply chain, hospitals , and providers of critical utilities.
Wizard Spider attacks tend to launch through spam and phishing using QBot and the SystemBC proxy. The group can also infiltrate businesses through compromised email threads between employees in Business Email Compromise (BEC) programs.
Once a crack in the door is present, the team will deploy Cobalt Strike and attempt to “grab” domain administrator privileges. The Conti ransomware strain is deployed, machines and hypervisor servers are encrypted , and a ransomware demand is created.
Victim management is done through a locker control panel.
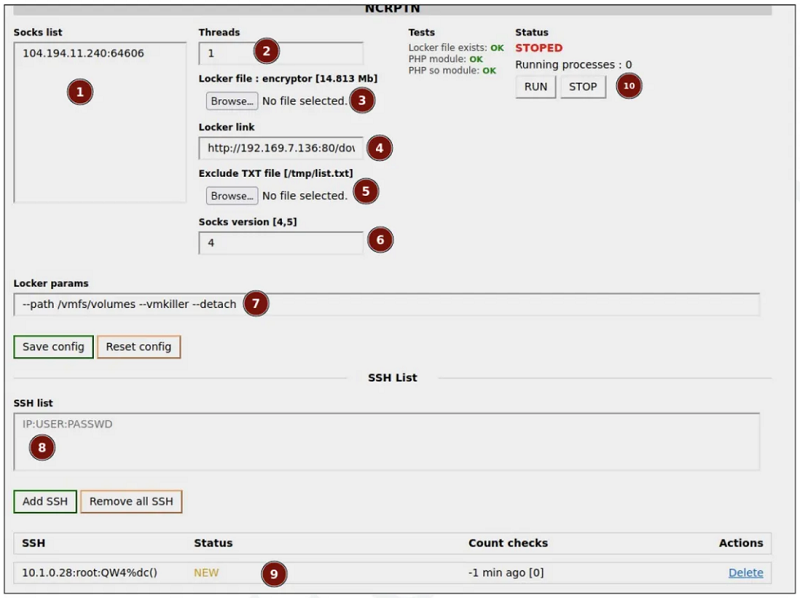
Wizard Spider uses both virtual private networks (VPNs) and proxies to hide its tracks. However, the group has also invested in some unusual tools, including VoIP and cold calling employees who call victims to scare them into paying after a security incident.
This is a tactic that has been used in the past by other ransomware groups, including Sekhmet, Maze , and Ryuk. Coveware suspects that this type of “call center” work may be outsourced by cybercriminals, as the templates and scripts used are often “the same.”
See also: WordPress: Millions of attacks target Tatsu Builder plugin
Several attack servers were also discovered containing a cache of tactics, techniques, exploits, cryptocurrency wallet , and encrypted .ZIP files containing notes made and shared by attack groups.
“The Wizard Spider team has proven capable of generating revenue from many aspects of its operations,” says PRODAFT.
Information source: zdnet.com
