

A new ransomware called “Hog” encrypts the devices of unsuspecting users and decrypts them only if they connect to its developer’s Discord server. A few days ago, MalwareHunterTeam discovered a (work-in-progress) decryptor for the Hog ransomware, which asks victims to connect to the hackers ’ Discord server to decrypt their files .
BleepingComputer spotted the ransomware's encryption component [VirusTotal], which, when executed, checks for the presence of a specific Discord server. If it does, it begins encrypting victims' files. While encrypting victims' files, it appends the .hog and automatically extracts the decryption component.
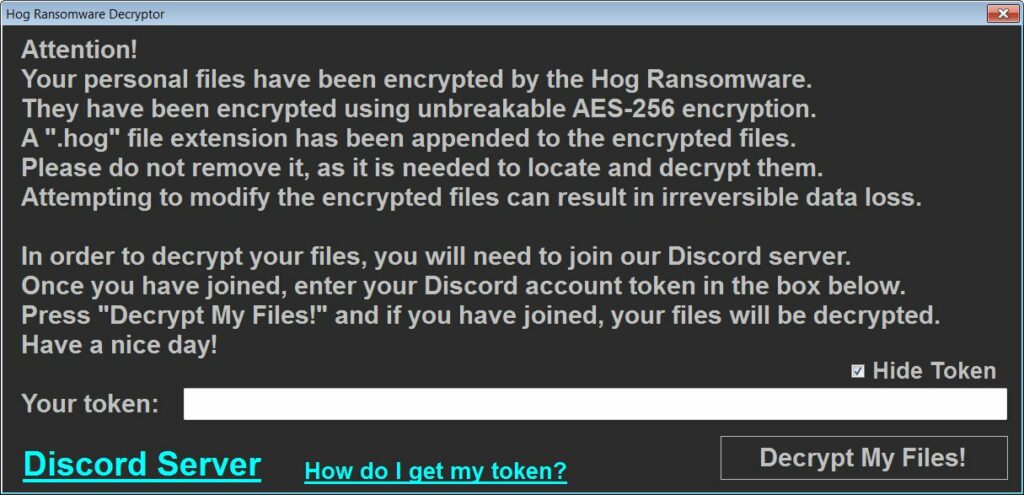
Once the ransomware has finished encrypting the device, it will launch the decryption program DECRYPT-MY-FILES.exe from the Windows Startup folder.
This decryptor will explain to victims exactly what happened and then ask them to enter their Discord user token.
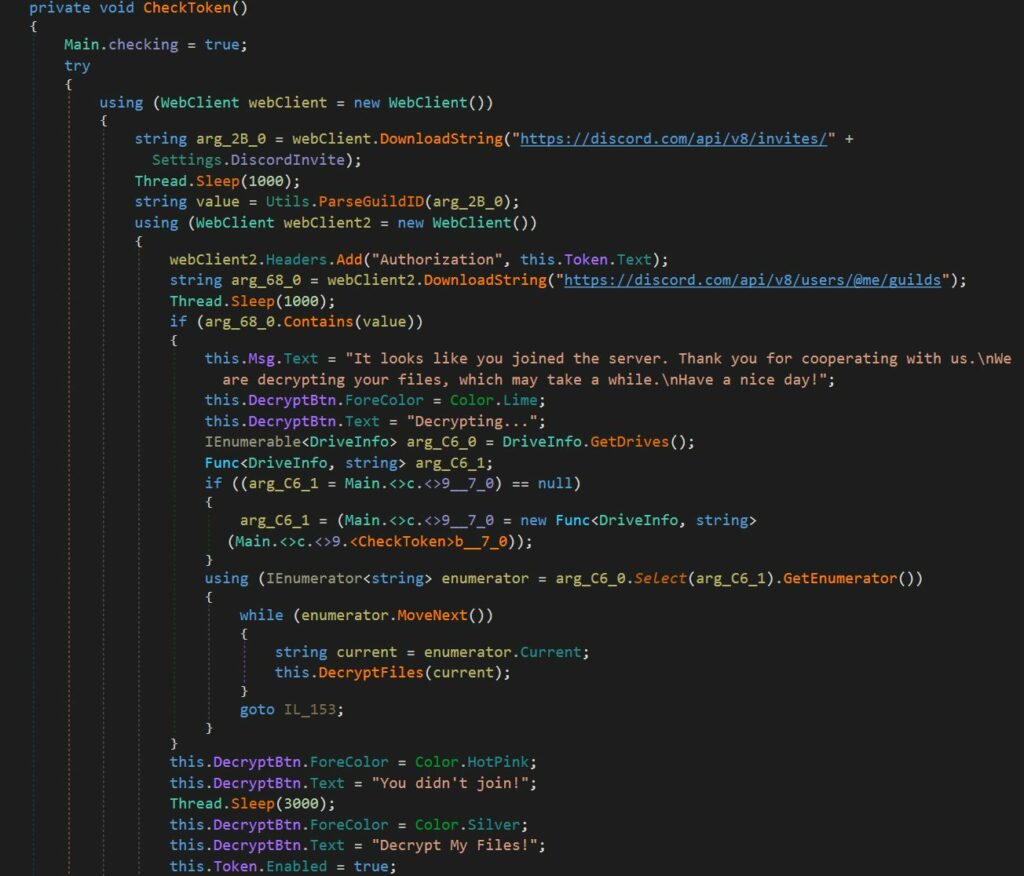
A Discord token allows the ransomware to verify Discord's APIs and to check if someone has connected to its server. If a victim has connected to the server, the ransomware will decrypt its files using a static key that is embedded in the ransomware.
Hog appears to be an ongoing ransomware, and simultaneously its case demonstrates that threat actors are increasingly using Discord for malicious activities.
Additionally, Trend Micro recently discovered another ransomware, dubbed “Humble,” which uses a webhook to post information about new victims to the malicious actor’s Discord server.
It is worth noting that Discord is commonly used by threat actors to distribute malware or collect stolen data . As malicious actors increasingly turn to Discord, it is important for network administrators and security tools to monitor Discord traffic for threats or other abnormal behavior.
Source: bleepingcomputer.com
