

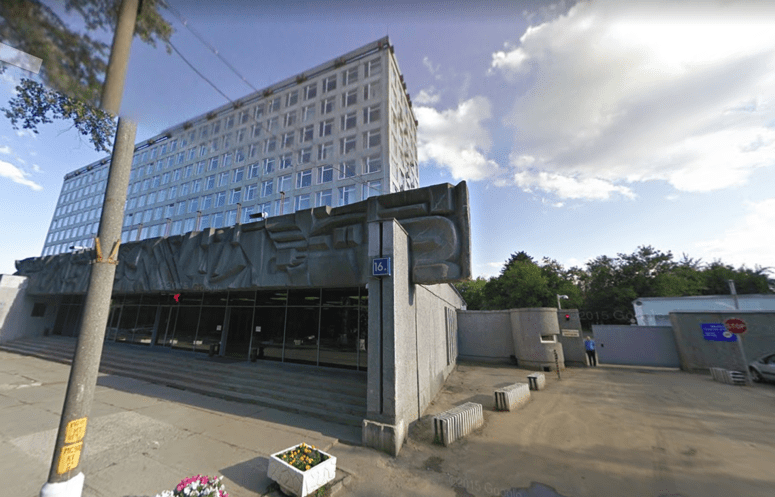
The US Treasury Department announced late last week sanctions on a Russian research institute allegedly involved in the development of Triton, a malware strain designed to attack industries. The institute is the State Research Center of the Russian Federation FGUP Central Scientific Research Institute of Chemistry and Mechanics, also known as CNIIHM or TsNIIKhM.
A report published in October 2018 identified CNIIHM as the likely creator of the Triton malware. The Triton malware, also known as Trisis or HatMan, was designed to specifically target a specific type of industrial control system (ICS) equipment: Schneider Electric Triconex Safety Instrumented System (SIS) controllers.
According to technical reports from FireEye, Dragos, and Symantec, the malware was distributed via phishing campaigns. Once it managed to infect a workstation, it would search for SIS controllers on network and then attempt to modify the controller's settings.
The researchers said that Triton contained instructions that could either stop a production process or cause machines controlled by the SIS to operate in an unsafe state, creating a risk of explosions, but also a risk to the lives of the people operating those machines.
The malware was first detected in 2017, after it was successfully used during a hack of a Saudi Arabian petrochemical plant owned by Tasnee. The attack nearly caused an explosion.
Since then, the malware has targeted numerous companies around the world. Additionally, the group behind it – known as TEMP.Veles or Xenotime – has targeted at least 20 US electric utilities, which it scanned for vulnerabilities.
The sanctions now imposed on the Russian research institute prohibit U.S. entities from interacting with the CNIIHM and also provide for the seizure of any assets the institute has in the United States.
Secretary Steven T. Mnuchin commented on the incident, stating that the Russian government continues to conduct dangerous cyber activities targeting the United States and its allies. He also stressed that the U.S. government will continue to protect the country's critical infrastructure from anyone who tries to disrupt it.
Earlier this week, the US Department of Justice filed charges against six hackers from the Sandworm group, who allegedly developed the NotPetya , KillDisk, BlackEnergy and OlympicDestroyer malware. At the same time, CISA and the FBI uncovered a recent hacking campaign , which was allegedly carried out by the Russian group “Energetic Bear”. The EU also imposed sanctions on two Russian military intelligence officers for their role in the 2015 hack of the German Parliament
However, as several security researchers pointed out on Twittershortly after the announcement of the sanctions imposed by the Treasury Department, the US may not benefit from this move, given that it has previously carried out attacks against industrial systems through the development of the Stuxnet malware against Iran's nuclear program in 2010.
