[su_heading]Sucuri's “Hacked Website Report – 2016/Q2” provides some very interesting data on the most popular content management platforms affected by hacking attacks, with WordPress being by far the most vulnerable platform at 74%.[/su_heading]
Three out of four hacked websites run on WordPress
According to the report's findings, things have not changed at all compared to the first half of 2016. Statistics show that WordPress is still the most vulnerable CMS platform, with the percentage of compromised websites reaching 74%.
This is partly justified by the fact that WordPress holds the lion's share of the market, with a percentage of more than 50%, and this is perhaps the reason why most hackers focus their efforts on it.
In addition to WordPress, the list of most vulnerable platforms is completed by Joomla (16%), Magento (5%), Drupal (2%), and vBulletin (0.32%).

When it comes to the percentage of compromised websites that hadn’t been updated to the latest version of the CMS, things were looking pretty rosy for WordPress compared to other platforms. Sucuri researchers found that 55 percent of WordPress websites hadn’t been updated to the latest version of the CMS, while for Magento, 96 percent of all websites were compromised because their owners had neglected to update them. The percentages of out-of-date Joomla and Drupal websites were 86 percent and 84 percent, respectively.
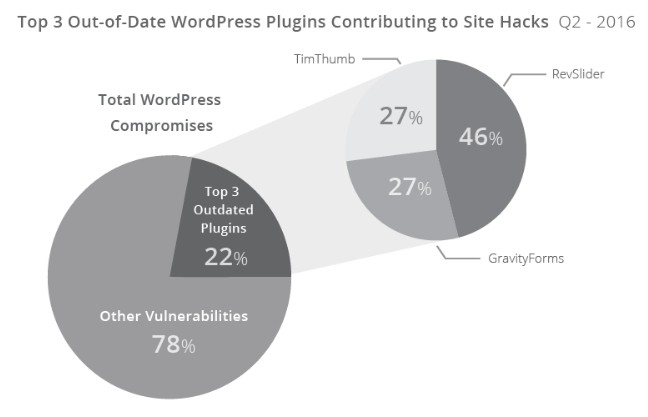
Another reason why WordPress has such a high number of compromised websites is that webmasters neglect to update plugins. Sucuri researchers revealed that a quarter of attacks against WP websites could be attributed to three plugins: TimThumb, GravityForms, and RevSlider.