FBI stops Dridex malware, which was designed to steal banking credentials
The United States Department of Homeland Security (DHS), in collaboration with the FBI and the Department of Justice (DOJ), has stopped a malware, which was designed to steal banking and other credentials from infected computers - botnet, called Drιdex.
A case has been filed against the Moldovan alleged administrator of the botnet, who is also known by the nicknames “Bugat,” “Cridex,” or “Drιdex.”
Andrey Ghinkul, also known as Andrei Ghincul and Smilex, 30, a Moldovan, was sentenced to nine years in prison in the Western District of Pennsylvania on charges of criminal conspiracy, unauthorized access to computers with the intent to cause damage to machines or defraud users, wire fraud and bank fraud.
Ghinkul was arrested on August 28, 2015 in Cyprus.
On February 13, the FBI released a technical report seeking to provide more information about the Drιdex botnet. The FBI estimates that US companies lost a total of about $10 million to Drιdex, and Ghinkul and his gang are accused of illegally transferring funds, specifically more than $3.5 million in two transactions in 2012, from an account at Penneco Oil's US bank to an account in a Russian bank.
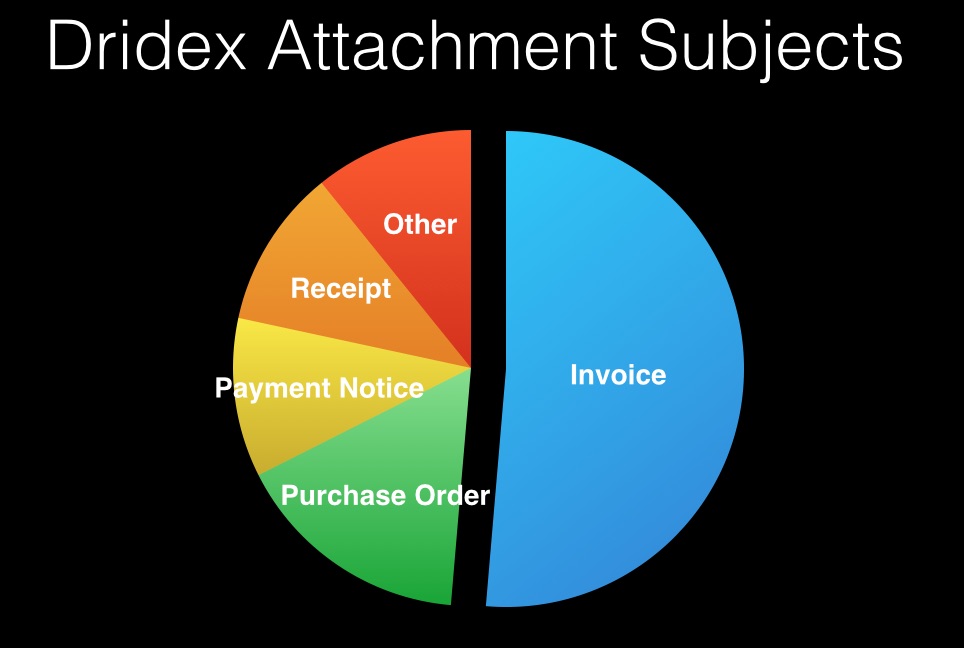
“Dridex is a multifunctional malware package that leverages Microsoft Office’s cloaked macros and extensible markup language (XML) files to infect systems. Its goal is to infect computers, steal credentials, and siphon money from victims’ bank accounts ,” the FBI said in a statement.

The malware has infected computers and systems in 27 countries around the world, including the US, Canada, UK, Ireland, France, Sweden, Germany, Norway, Austria, the Netherlands, Italy, Belgium, Bulgaria and Romania, the United Arab Emirates, Qatar, Israel, Indonesia, Singapore, Malaysia, Hong Kong, China and India, Vietnam, Australia and New Zealand.