

 Trusteer researchers report that the latest victims of the Citadel Trojan include one of the world's largest petrochemical companies.
Attackers, like so many others, target critical organizational infrastructure using phishing campaigns to steal network credentials.
Researcher Dana Tamir said attackers are targeting webmail URLs to infect staff.
“To steal login credentials that provide access to the company’s webmail system, the malware looks for URLs like ‘https://mail.target-company.com’, which would be the login URL of the webmail system,” Tamir said.
“When the user submits their login credentials, the malware intercepts the username, password, and any other information submitted during the login process.”
Citadel It is updated regularly and even offers a full support system for customers who have purchased licenses.
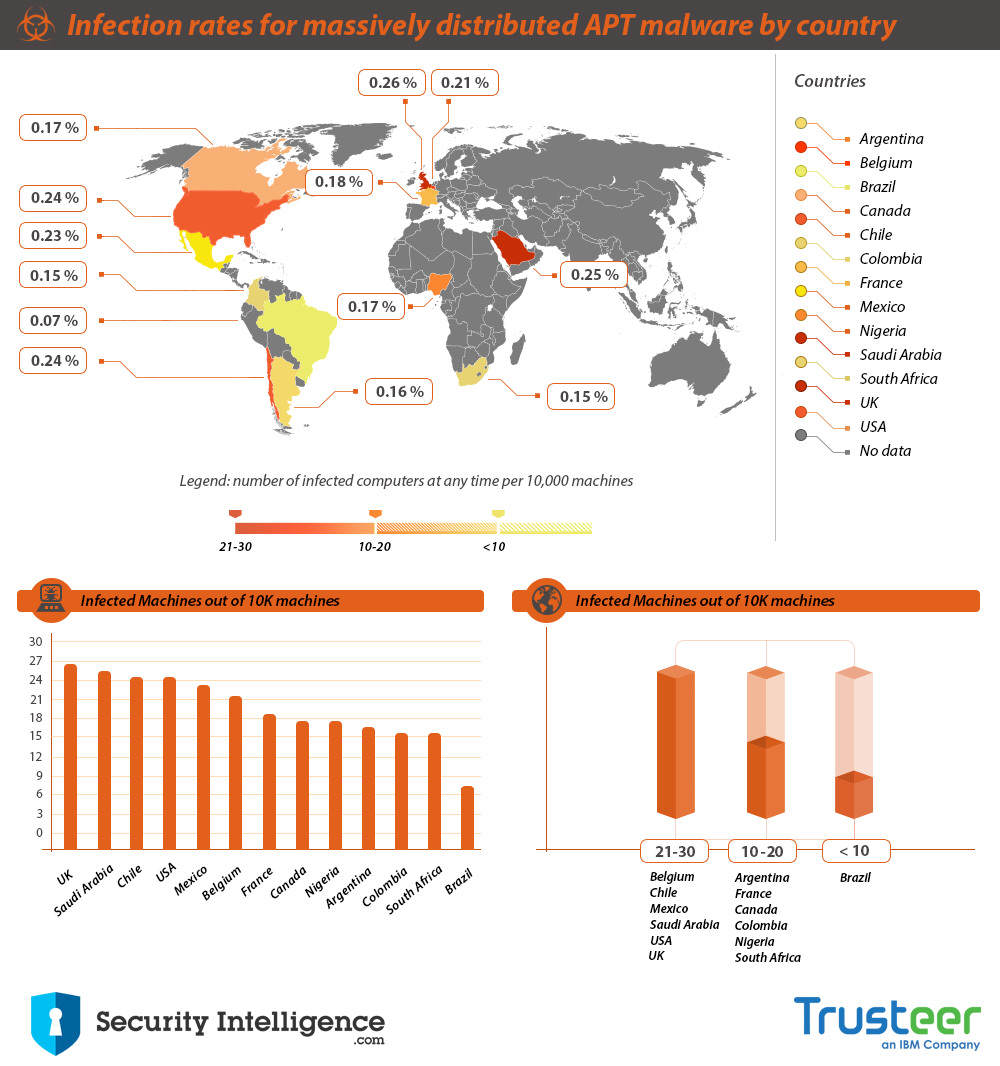
Tamir called the Citadel and many others like it a "mass malware distribution" attack that aims to infect as many machines as possible.
