

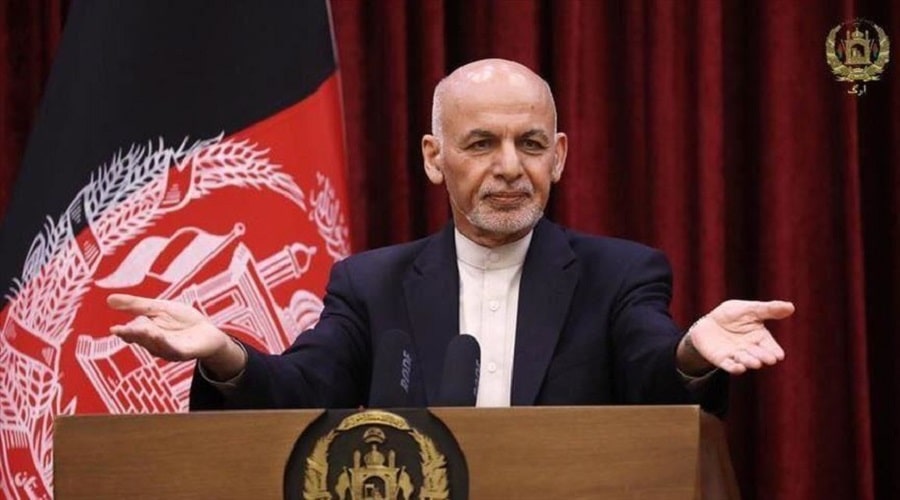
Chinese hackers are carrying out continuous cyberattacks targeting the Afghan government, using the country's president, Ashraf Ghani,.

On Thursday, Check Point Research (CPR) reported that the Office of the President of Afghanistan, representing President Ashraf Ghani, is being used as bait in a phishing campaign aimed at gaining access to government services in the country. One of the phishing attacks targeting the Afghan National Security Council (NSC) was successful , and Chinese hackers breached the systems.
See also: Japanese government agencies breached via Fujitsu hack
It is believed that an APT group, called IndigoZebra , is behind the phishing attacks in Afghanistan .
The samples of phishing emails seen by the researchers purport to come from the office of the Afghan President and request an urgent review of amendments to a document regarding an upcoming press conference.
See also: Chinese hackers spent 3 years developing backdoor to spy on governments
The file attached to the email is password-protected and is a .RAR archive named NSC Press conference.rar. If the victim opens the file, they receive a Windows executable (NSC Press conference.exe), which deploys a malware dropper and the “xCaon” backdoor, which maintains persistence by setting a registry key.
The backdoor can download and upload files, execute commands, and steal data.
Chinese hackers are also abusing Dropbox as a form of C2 server in the latest version of this backdoor, dubbed “BoxCaon” by Check Point Research.
The security firm says that by using the Dropbox API, hackers are “hiding their malicious activities.”
The IndigoZebra hacking group is also developing a NetBIOS scanning tool that has been adopted by another Chinese APT group, APT10 or Stone Panda, to target other victims.
See also: Russian hackers behind massive spear-phishing campaign that hit Ukraine
The malware used by Chinese hackers also includes Meterpreter, Poison Ivy, xDown and xCaon backdoor.
Check Point Research reports that the APT group in question is also likely responsible for attacks dating back to 2014 that targeted political entities in Kyrgyzstan and Uzbekistan.
Researchers commented that the phishing attacks on the Afghan government show that Chinese hackers IndigoZebra are aggressively continuing their attacks and expanding to new targets, with a new set of tools.
Source: ZDNet
