

FireEye/Mandiant security researchers have discovered that an affiliate of the DarkSide ransomware gang , known as “UNC2465 ,” has carried out a supply chain attack against a CCTV camera vendor . UNC2465 is said to be a key partner of the DarkSide gang , along with other gangs that Mandiant has designated as “UNC2628” and “UNC2659 . ”
The attackers compromised the vendor's site and implanted malicious code into a Windows application, a customized version of the Dahua SmartPSS Windows, which the company provides to its customers to control their security feeds.
Read also: Colonial Pipeline: Most of the ransom paid to DarkSide recovered
Specifically, Mandiant stated the following: “The attack detailed in this post began on May 18, 2021, just days after the DarkSide operation was shut down. While no ransomware was observed, Mandiant believes that the gangs that have carried out attacks with DarkSide may be using multiple ransomware affiliates and can switch between them at will. At some point in May 2021 or earlier, UNC2465 likely trojanized two software installation packages on the site of a CCTV security camera provider.”
The site was first breached on May 18 and the hackers remained within the company until early June, when Mandiant researchers discovered the supply chain attack.
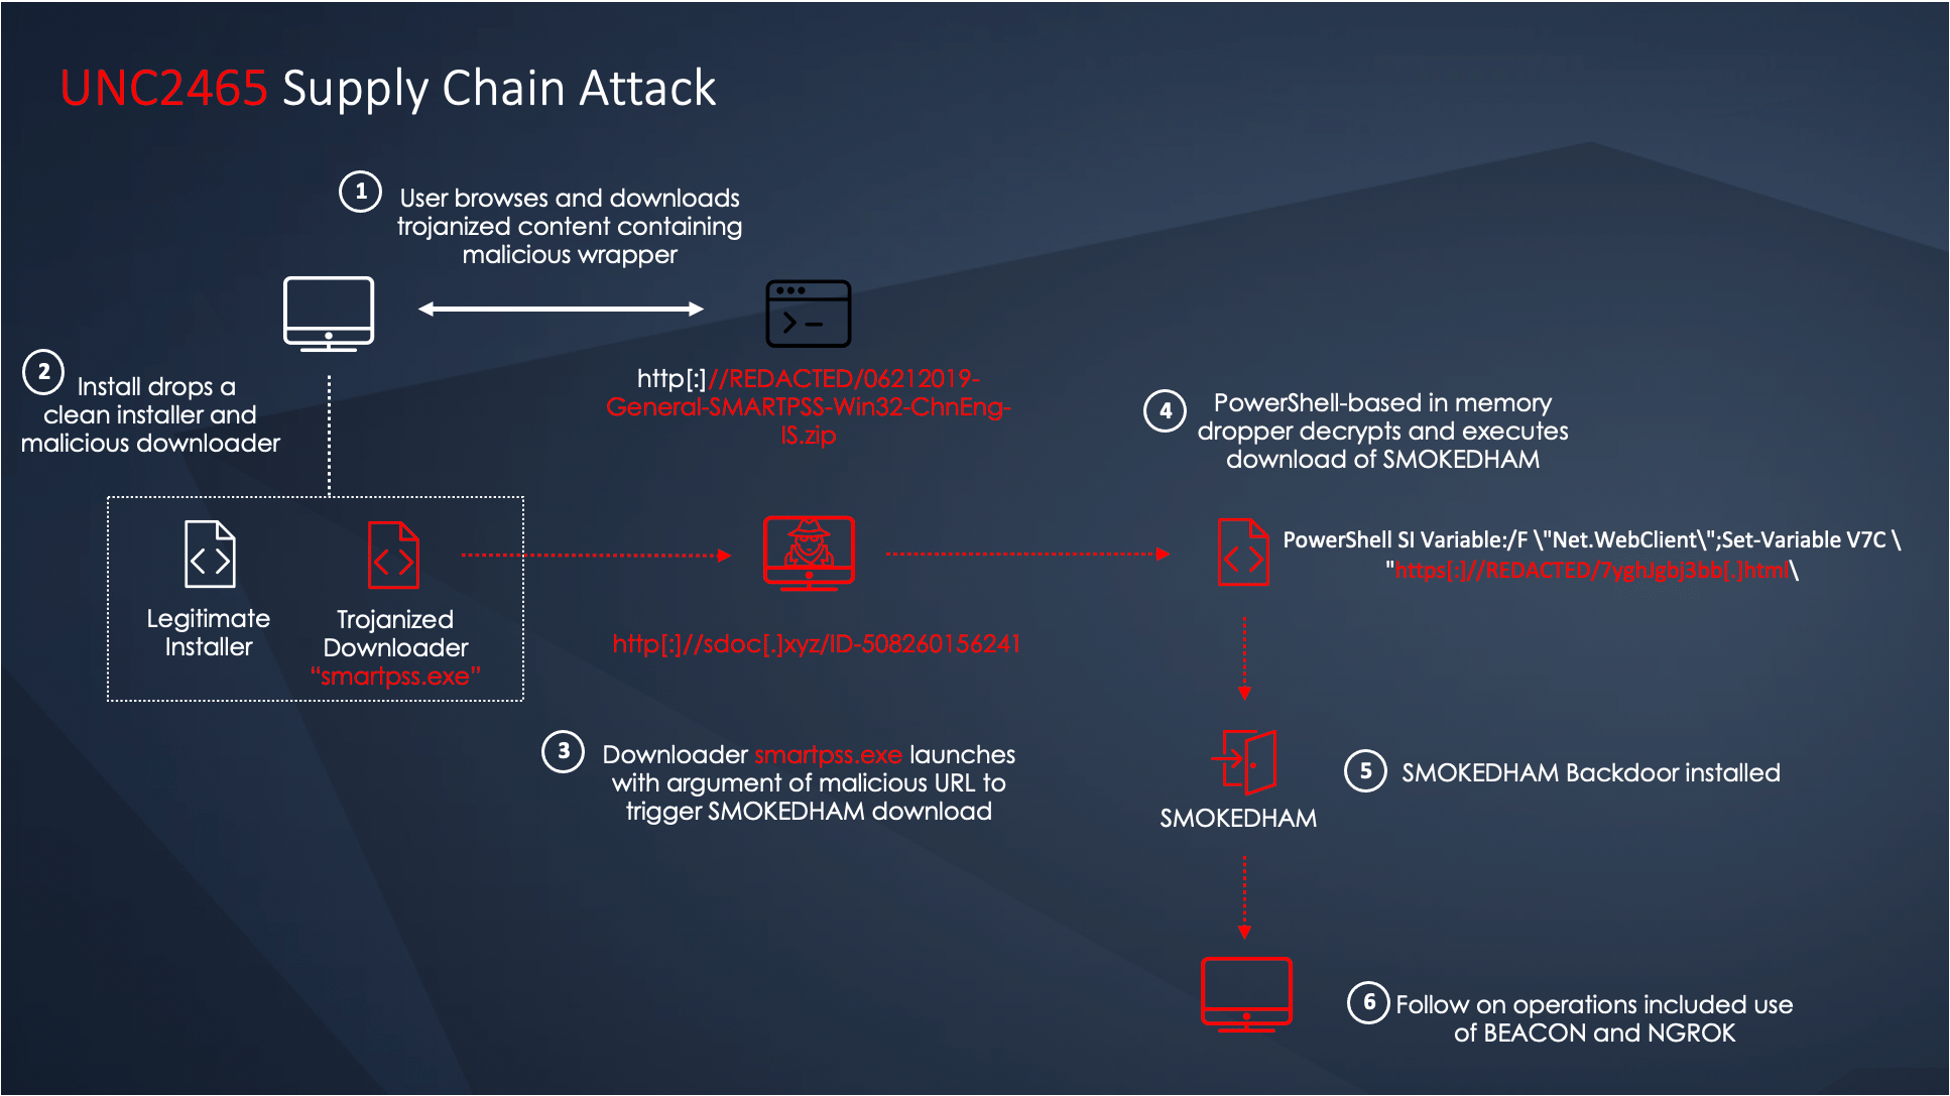
The infected application was used by attackers to distribute a version of the .NET SMOKEDHAM backdoor, which supports keylogging, screenshot capture, and execution of arbitrary commands on infected systems.
Mandiant observed the trojanized installer being downloaded to a Windows workstation after the user visited a legitimate site that the victim organization had previously used. The company confirmed that the user intended to download, install, and use the SmartPSS software. The figure below shows an image of the download page used for the SmartPSS software.
See also: DarkSide ransomware operation shut down – associates complain they haven't been paid
FireEye researchers linked the SMOKEDHAM backdoor to the UNC2465 group, which has been active since at least April 2019 and is considered an affiliate of DarkSide's RaaS operation.
In this attack, once the backdoor was deployed, UNC2465 created an NGROK tunnel and moved laterally in less than 24 hours. Five days later, the UNC2465 hackers returned and used additional tools – such as a keylogger and Cobalt Strike BEACON – to steal credentials by dumping LSASS memory.
The researchers also noted that in this supply chain attack, UNC2465 did not distribute the DarkSide ransomware as the final payload, but they did not rule out the possibility that the cybercriminal group has integrated into a new RaaS operation.
Proposal: Manchester is under 'coordinated global attack' by hackers
Experts recommend scanning internal networks for the SmartPSS application and searching for indicators of compromise related to the SMOKEDHAM backdoor. Finally, the researchers' report notes the following:
“UNC2465’s shift from drive-by attacks on website visitors or phishing emails to this software supply chain attack represents a worrying shift that brings new challenges. While many organizations are focusing more on perimeter defense and two-factor authentication (2FA) following recent public examples of password reuse or VPN device exploitation, endpoint monitoring is often overlooked or limited to standard antivirus. A comprehensive security program is essential to mitigate the risk from sophisticated groups like UNC2465 as they continue to adapt to a changing security landscape.”
Information source: securityaffairs.co
