

A new vulnerability has been discovered in Samsung SmartCam, allowing attackers to gain root access to the device and execute commands remotely.
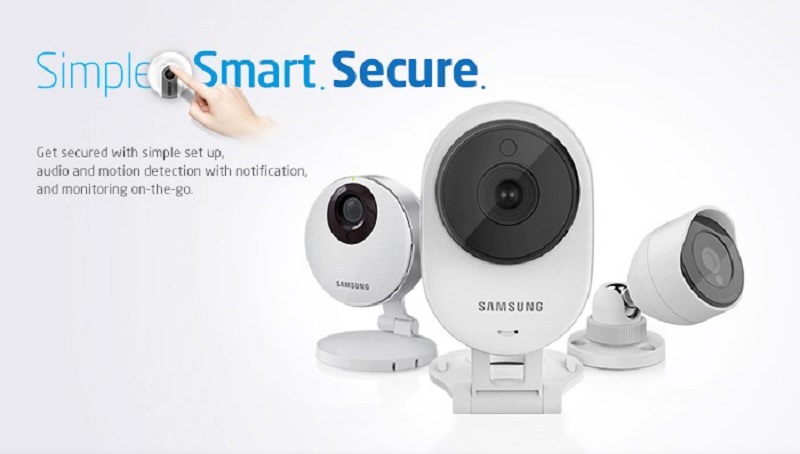
Samsung SmartCam is essentially an IP camera that allows you to connect to your own Samsung services and view live video or recorded events from any location. It offers baby or pet monitoring, business and home security with super-easy, real-time configurations.
But one of the problems with SmartCam is its questionable security, as vulnerabilities in software have already been discovered several times in the past. And a new one is making the rounds these days.
exploitee.rs has uncovered a vulnerability that could allow an attacker to gain root access to the device, using a web server that Samsung reportedly left behind after trying to address previous vulnerabilities.
Specifically, the company attempted to patch security holes in the device by removing the local web interface and forcing users to access the SmartCloud website, but at the same time the company also left the local server running. And as it turns out, the vulnerability allows an attacker to connect to that web interface by clicking a custom firmware file.
Samsung has not yet addressed a patch for this new vulnerability, but it goes without saying that a new firmware should be delivered as soon as possible.
In the meantime you can find additional interesting information, including a proof of concept plus a workaround to fix the vulnerability without an official patch on the SmartCam exploitee wiki page which details the flaw.
