

An international law enforcement operation has shut down AVCheck, an online service used by cybercriminals to test whether their malware is detected by antivirus software (before using it in real attacks).
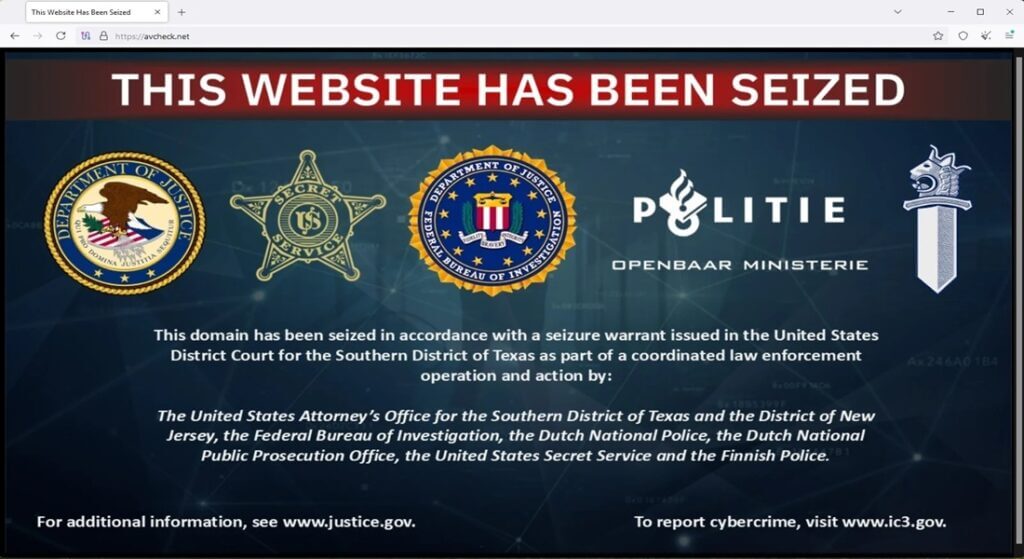
The platform's official website, avcheck.net, has now been replaced by a seizure banner, bearing the logos of the US Department of Justice, the FBI, the Secret Service, and the Dutch Police (Politie).
According to a statement from Dutch authorities, AVCheck was considered one of the largest CAV (Counter AntiVirus) services internationally, facilitating testing of malware hiding from security tools. Its use by cybercriminals was intended to ensure that their attacks would go unnoticed by victims.
See also: APT41 – ToughProgress malware: Abuse of Google Calendar for C2 purposes
"The shutdown of AVCheck is a crucial step in the fight against organized cybercrime," said Matthijs Jaspers from Politie. "With actions like this, we stop cybercriminals before they even start their attacks, while also protecting future victims."
During the investigation, authorities identified links between the management of AVCheck and two crypting services: Cryptor.biz and Crypt.guru. The former has also been seized, while the latter has been taken down. These services are used to disguise the true nature of malware, making it indistinguishable from antiviruses. The combined use of crypting services and tools like AVCheck is a standard tactic in the arsenal of cybercriminals.
Before the official seizure, authorities had posted a fake login page on the AVCheck website, warning users of the legal consequences of using the service.
The dismantling of the AVCheck service and related crypting platforms is a key victory against organized cybercrime, according to a statement from the US Department of Justice, released on May 27, 2025.
See also: New self-propagating malware infects Docker Containers
“Cybercriminals don’t just create malware, they refine it for maximum destruction,” said FBI Special Agent Douglas Williams. He said the attackers were exploiting CAV services to customize their malware, ensuring it would evade the most advanced security systems, evade detection, and cause widespread damage.
The investigation that led to the dismantling of AVCheck involved an undercover operation in which agents pretended to be customers and made purchases from the illegal services. This tactic allowed authorities to obtain evidence about the platform's operation and confirm its criminal nature.
As mentioned in the official announcement of the Department of Justice, researchers analyzed data, including communication emails, revealing direct links to known ransomware gangs that have targeted both American and international organizations.
The action is part of the broader Operation Endgame, an international campaign to suppress digital crime that has already led to the seizure of more than 300 servers and 650 domains used to facilitate ransomware attacks.
As part of the same operation, the infrastructures of malware such as Danabot and Smokeloader, two of the most widespread tools in the cybercriminal toolbox, have previously been disrupted.
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
See also: Google Ads spread malware via fake Homebrew Site
This operation does not eliminate cybercrime, but it strikes at critical elements of the attack chain, specifically the infrastructure. Rather than just hunting down “malicious payloads,” authorities have targeted the testing platforms that help them go unnoticed. This is a strategic blow to an underground ecosystem that has until now operated with relative impunity.
At the same time, the partnership between the US, FBI, Dutch police and other agencies shows that cybercrime is no longer addressed in isolation — it requires coordinated global action.
Source: www.bleepingcomputer.com
