

The well-known online store selling stolen credit cards, Rescator.cc, is so overwhelmed by recent high-profile breaches that it has begun reducing its prices due to overload.
The site essentially mocks the security of some of the world's largest retailers, many of which have been attacked by hackers in recent months, resulting in the theft of millions of customers' credit card details.
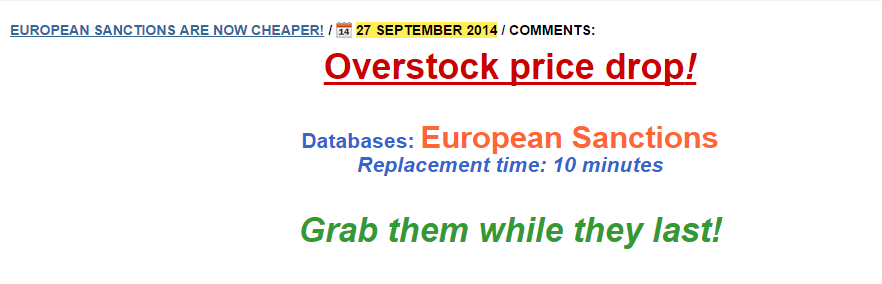
Target stores in the US, along with Sally Beauty and Home Depot, were among the high-profile organizations known to have millions of customer cards added to the Rescator store. It is certain, of course, that many companies have been breached without publicly reporting it.
Many of the recent breaches are related to malware like BlackPOS, which loads onto card payment terminals in stores.
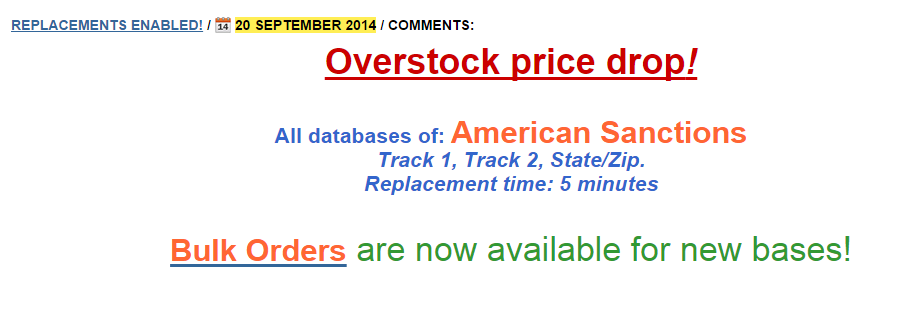
The stolen cards were posted on the page in installments, labeled American Sanctions and European Sanctions, and could be purchased in batches and filtered by geography to reduce the likelihood of detection in a buyer's subsequent malicious transactions.
The shadowy figure behind Rescator, according to cyber researcher Brian Krebs, is likely Andrew Hodirevski, a Ukrainian. The hacker offered Krebs $10,000 to keep quiet about his story, which exposed him.
