

A threat actor referred to as “RomCom” has targeted pro-Ukrainian organizations and guests of the upcoming NATO Summit, which begins today in Vilnius, Lithuania.
BlackBerry's research and intelligence team recently discovered two malicious documents that pretended to be the organization of the Ukraine World Congress and topics related to the NATO Summit in order to attract selected targets.
The attackers used a copy of the Ukrainian World Congress website hosted on a “.info” domain instead of the real one, which uses a “.org” top-level domain.
The downloaded documents contain malicious code that exploits the RTF file format to initiate connections to external resources, ultimately loading malware onto the victim 's system .
See also: The number of email phishing attacks increased by 464%

Blurred RomCom background
In August 2022, Unit 42 first discovered the RomCom malware and linked it to an affiliate of the Cuba Ransomware. The Computer Emergency Response Team of Ukraine (CERT-UA) appeared to agree with this assessment based on its report in October 2022.
However, BlackBerry's analysis from that time indicated that the threat actors behind RomCom follow a rather global targeting approach, emphasizing that the Cuba ransomware never had a slant toward hacktivism.
In November 2022, the cybersecurity firm discovered a new RomCom campaign that abused software brands and used fake websites in English and Ukrainian to target unsuspecting victims with malicious installers.
More recently, in May 2023, a Trend Micro report on the latest RomCom campaign showed that threat actors were now impersonating legitimate software like Gimp and ChatGPT or creating fake software developer websites to promote their backdoor to victims via Google and black SEO techniques.
See also: Cyberbullying cases are constantly increasing
Latest campaign details
The latest campaign analyzed by BlackBerry uses download links to a typographical domain for the Ukraine World Congress website, which was likely promoted via spear-phishing, to infect visitors with malware.
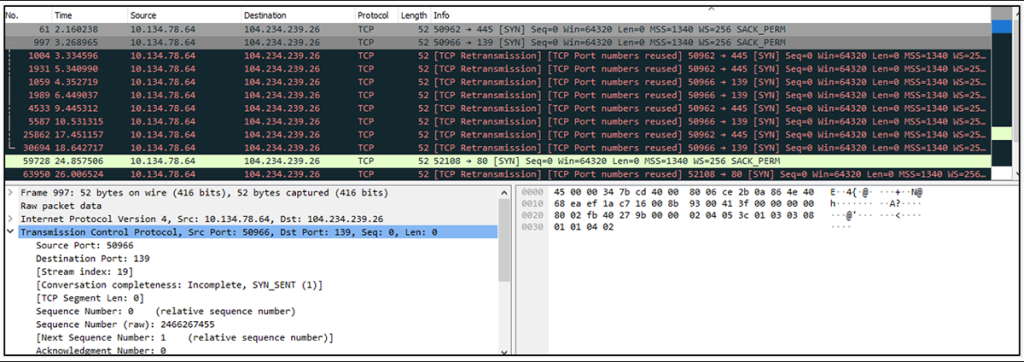
Documents downloaded from the fake website initiate an outbound connection at startup and download additional components from the attacker's command and control (C2) server.
The additional component observed during the investigation was a script that exploits the Follina vulnerability (CVE-2022-30190) from the Microsoft Support Diagnostic Tool (MSDT).
The final step of the attack is loading the RomCom backdoor onto the machine, which arrives in the form of an x64 DLL file named "Calc.exe.".
RomCom connects to the C2 to register the victim and sends back details such as the username, network adapter , and the size of the compromised computer's RAM.
The backdoor eventually writes the file “security.dll” to run automatically on reboot to persist and wait for commands from the C2. Based on previous reports, these commands include data exfiltration, downloading additional payloads, deleting files or directories, creating processes with fake PIDs, and launching a reverse shell.
See also: Mario Kart and Resident Evil: The Last Stand cameras
BlackBerry believes the campaign analyzed is either a RomCom operation with a new name or an operation involving key members of the old group supporting the new threat activity.
The researchers' report includes indicators of compromise for the decoy documents, the second-stage malware, the IP addresses , and the domains used for the campaign.
Information source: bleepingcomputer.com
