

A new information stealer called Stealc has appeared on the dark web and is gaining notoriety due to its aggressive promotion of theft capabilities and similarities to similar malware such as Vidar, Raccoon, Mars, and Redline.
Security researchers at cyber threat intelligence firm SEKOIA spotted the new strain in January and noticed it began attracting users in early February.

New stealer for sale
Stealc has been advertised on hacking forums by a user named “Plymouth,” who presented the malware as a piece of malware with extensive data-stealing capabilities and an easy-to-use admin panel.
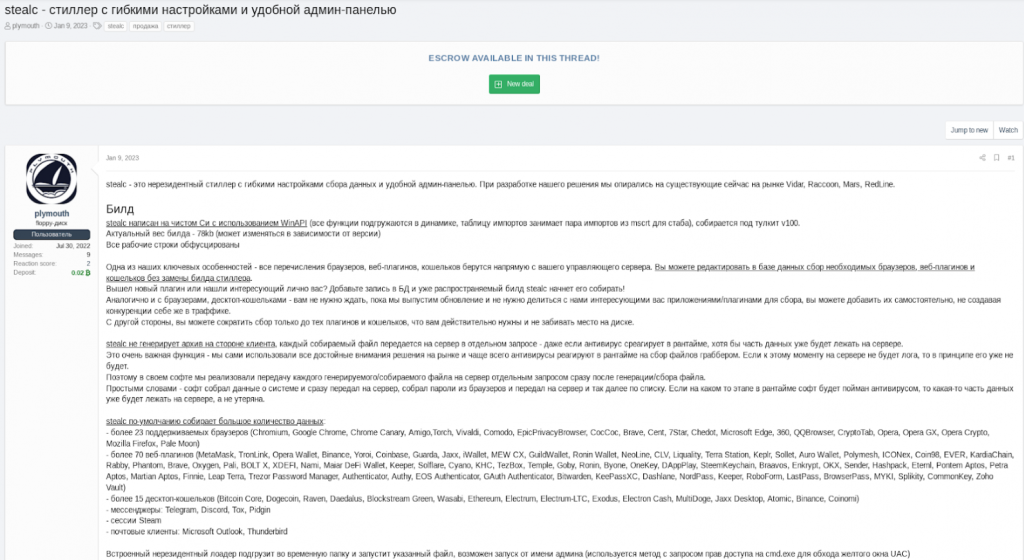
According to the advertiser, in addition to the typical targeting of web browser data, extensions, and cryptocurrency wallets, Stealc also features a customizable file downloader that can be configured to target whatever file types the operator.
After the initial post, Plymouth began promoting the malware on other hacking forums and private Telegram, offering test samples to potential customers.
The vendor also created a Telegram channel dedicated to publishing the changelogs of the new version of Stealc, with the most recent being version 1.3.0, released on February 11, 2023. The malware has been actively developed and a new version appears on the channel every week.
Plymouth also said that Stealc was not developed from scratch, but was based on Vidar, Raccoon, Mars and Redline.
A common feature that researchers found between Stealc and the Vidar, Raccoon, and Mars infostealers is that they all download legitimate third-party DLLs (e.g. sqlite3.dll, nss3.dll) to help steal sensitive data.
In a report today, SEKOIA researchers note that the command and control (C2) communications of one of the samples they analyzed shared similarities with those of the info-stealers Vidar and Raccoon.
Researchers discovered more than 40 C2 servers for Stealc and several dozen samples in which it is used, indicating that the new malware has attracted the interest of the cybercriminal community.
This popularity may be due to the fact that customers with access to the admin panel can create new stealer samples, which increases the chances of the malware to a wider audience.
Despite the poor business model, SEKOIA believes Stealc poses a significant threat as it could be adopted by less technical cybercriminals.

Stealc's functions
Since its initial release in January, Stealc has added a number of cutting-edge features, such as the ability to randomize C2 URLs, improved log management with improved search and sorting capabilities, and the exclusion of victims located in Ukraine.
Weighing in at just 80KB, Stealc is a lightweight malware that exploits legitimate third-party DLLs written in C and abuses Windows API functions. The strings used are obfuscated with RC4 and base64 encryption – making it difficult to detect! Not stopping there, the malicious code automatically extracts stolen data from 22 web browsers, 75 plugins, and 25 desktop wallets.
SEKOIA's current report does not include all the data obtained from reverse engineering Stealc, but it provides an overview of the main steps of its execution.
Information source: bleepingcomputer.com
