

Tyler Technologies, a leading provider of technology services to the US government, has been hit by a ransomware attack, causing it to shut down. Tyler Technologies is one of the largest software and technology services companies in the US. The company, which provides technical services to local governments in several US states, employs 5,500 people and has projected 2020 revenue of approximately $1.2 billion.
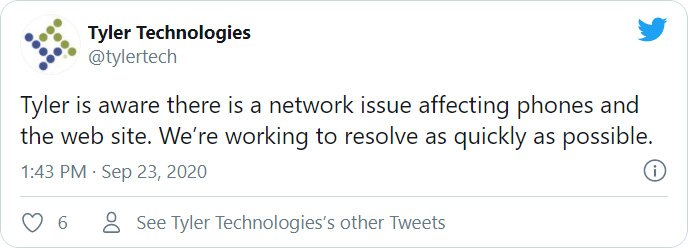
The company's official website began displaying a maintenance message, while its Twitter wrote that the company's systems were experiencing some technical problems.
Additionally, Matt Bieri, CIO of Tyler Technologies, sent an email to the company's customers, informing them that the company is currently investigating a cyberattack that affected its telephone and IT systems, noting that it has already notified authorities about the incident, while also working with independent IT experts.
Bieri also said in the email that the company discovered yesterday morning that an unauthorized attacker had disrupted access to some of its internal systems. The company has closed off access to external systems and is immediately investigating and remediating the issue. Security experts are assisting the company in investigating the incident and safely restoring the affected equipment. The company is also implementing enhanced monitoring systems. Bieri also said that current investigations indicate that the attack was limited to Tyler Technologies’ local network.
In posts on the Municipal Information System of California (MISAC) forum obtained by BleepingComputer, users have heard that Tyler Technologies has been hit by a ransomware attack that affected its phone ticketing and technical support systems. However, according to reports, the ransomware attack does not appear to be affecting the company's customers.
Security researchers said that the US government technology services provider has been attacked by RansomExx ransomware. RansomExx is a variant of Defray777 ransomware and has been active since June, when its operators attacked the Texas Department of Transportation (TxDOT), Konica Minolta and most recently IPG Photonics.
BleepingComputer spotted an encrypted file uploaded to VirusTotal yesterday related to the attack in question. This encrypted file has the extension “.tylertech911-f1e1a2ac” and includes the name Tyler Technologies, which is the same format used in other attacks . The RansomExx gang doesn’t have a data, but that doesn’t mean it doesn’t steal unencrypted files before deploying its ransomware.
