

Pharmaceutical services provider PharMerica has disclosed a massive data breach affecting over 5.8 million patients, exposing their medical data to hackers.
PharMerica is a provider of pharmaceutical services in 50 U.S. states, operates 180 local and 70,000 supply pharmacies, and serves 3,100 medical facilities nationwide.
According to a data breach notification filed with the Maine Attorney General's Office, hackers breached PharMerica's system on March 12, 2023, stealing the full names, addresses, dates of birth, social security numbers (SSN), medications, and health insurance information of 5,815,591 individuals.
The company discovered the breach on March 14, 2023, and its investigation determined on March 21 that customer data had been stolen. However, notifications of the data breach were not sent to affected individuals until last Friday, May 12, 2023.
See also: Philadelphia Inquirer: Its operations were interrupted due to a cyberattack

See also: Lancefly hacking group uses MerDoor malware
Data leak by hackers
Although PharMerica does not mention the type of hacking incident, the Money Message ransomware gang claimed to have carried out the attack on March 28, 2023, when it began publishing the stolen data.
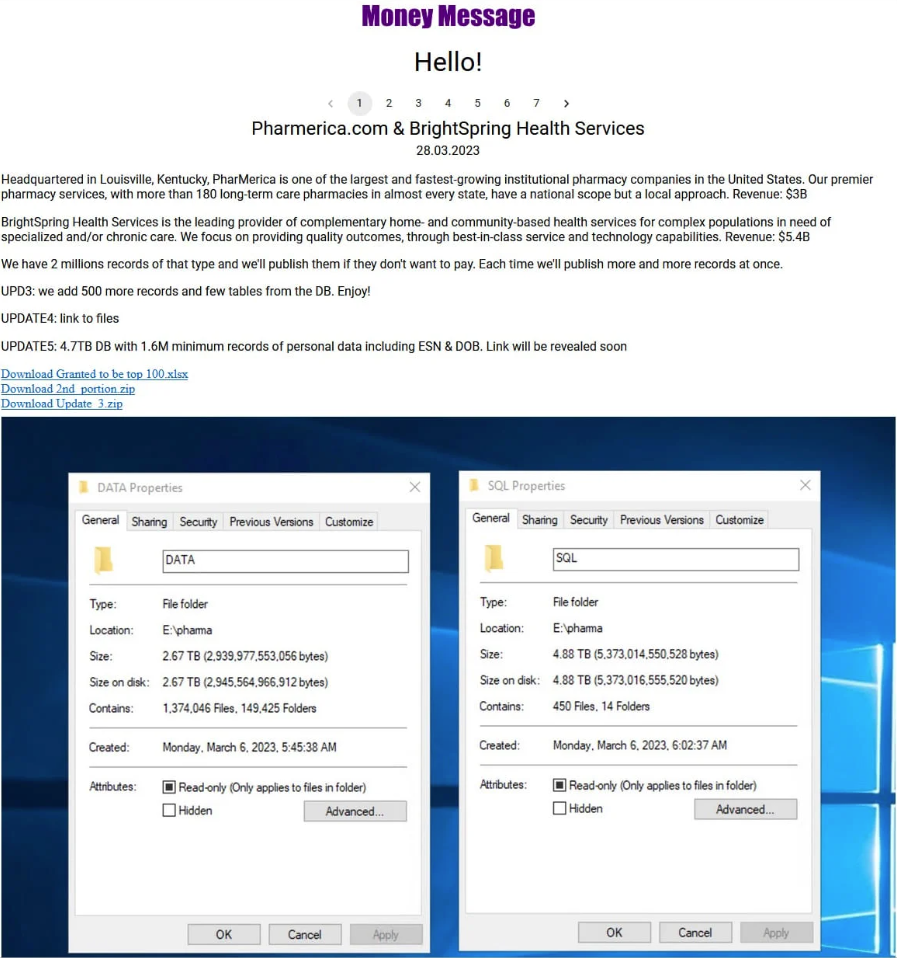
Along with PharMerica, the threat actors also listed BrightSpring, a healthcare provider that merged with PharMerica in March 2019.
Message Money claimed to have stolen 4.7TB of data during its attack on PharMerica, stating that it consisted of at least 1.6 million unique records of personal information.
On April 9, 2023, the timer expired and the threat actors published all the stolen data, as they claim, on their extortion website. Unfortunately, the files are still available for download at this time.
See also: RA Group ransomware: Targets companies in the US and South Korea
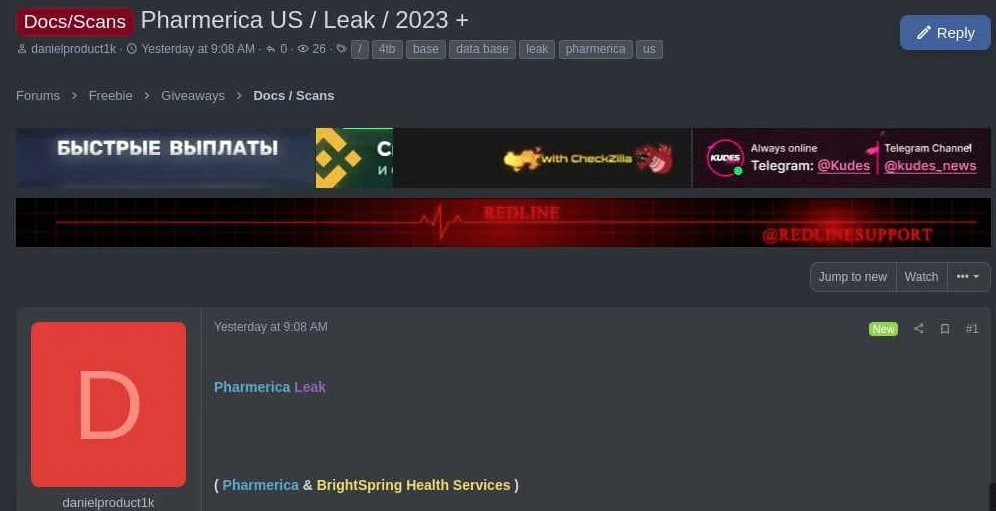
To make matters worse, a threat actor has already posted the entire data dump on a clearnet hacking forum, breaking the file into thirteen parts for easier download.
Money Message, a new ransomware operation that began around March 2023, gained media attention for its breach against Taiwanese computer component manufacturer MSI (Micro-Star International).
Information source: bleepingcomputer.com
