

[su_heading size=”18″ margin=”40″]A critical security flaw in the popular video streaming service allowed any attacker to download the entire source code of Vine from its servers.[/su_heading]
[su_spacer][su_spacer][/su_spacer]The issue was discovered by security researcher and well-known vulnerability hunter, Avicoder, and reported on Twitter on March 31. By exploiting the vulnerability in question, the white-hat hacker was able to access and download the entire source code of Vine, with great ease.
[su_note note_color=”#aacca8″ radius=”7″]The popular video streaming service, which allows sharing videos of a maximum duration of 6 seconds, was acquired by Twitter in 2012.[/su_note]
It all started when the researcher discovered a security flaw, and managed to download the Docker image with the application's source code.
[su_spacer][su_spacer][/su_spacer]
Docker is a widely used platform for building, running, and managing applications. While Docker installations are typically not accessible to the public due to the sensitive nature of the content they handle, the same was not true for Vine.
Taking advantage of this fact, Avinash used Censys.io, a new search engine exploited by hackers, locating more than 80 docker images online.
[su_spacer][su_spacer][/su_spacer]
“Censys.io gave me a very interesting URL in its results: https://docker.vineapp.com,” the researcher says. “Since this Docker should theoretically be private, why was it available online? It should be. Searching for /* private docker registry */ I found that this particular docker provides functionality that allows developers to host and share images over the internet.”.
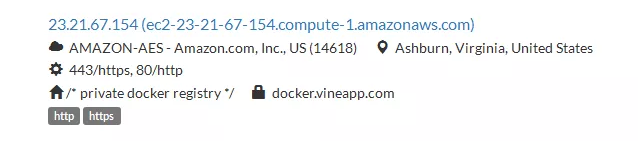
The researcher downloaded the image named “vinewww,” which was related to the Vine application, and examined it through a docker image viewer.
He couldn't believe what he had just discovered. The entire source code for Vine was displayed on his screen.
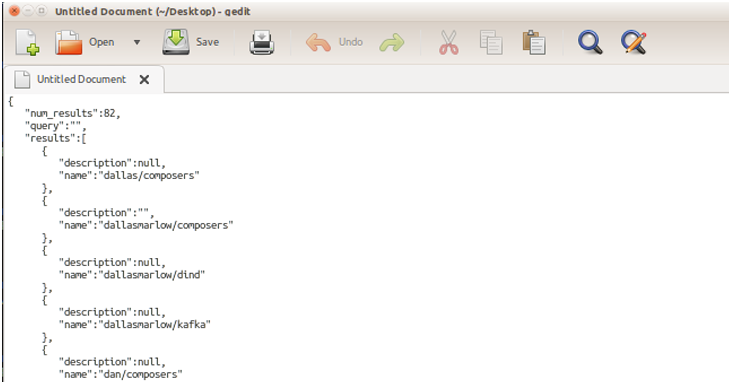
“I was able to see the entire source code of Vine, its API keys as well as third party keys and secrets,” Avicoder explains. “Even when running the image without any parameters, I was able to run a copy of Vine locally.”.
[su_spacer][su_spacer][/su_spacer]
[su_note note_color=”#f6f9f8″ radius=”7″]The researcher tweeted his findings, and five minutes later, the issue was fixed. The company rewarded the researcher with $10,080.[/su_note]
📧
Subscribe to the SecNews Newsletter
